Zanshin Release Notes
Learn about new features, changes, and improvements to Zanshin.

Zanshin news and updates | September 2026
Details of the New Features
1. SAQ Grading and Review
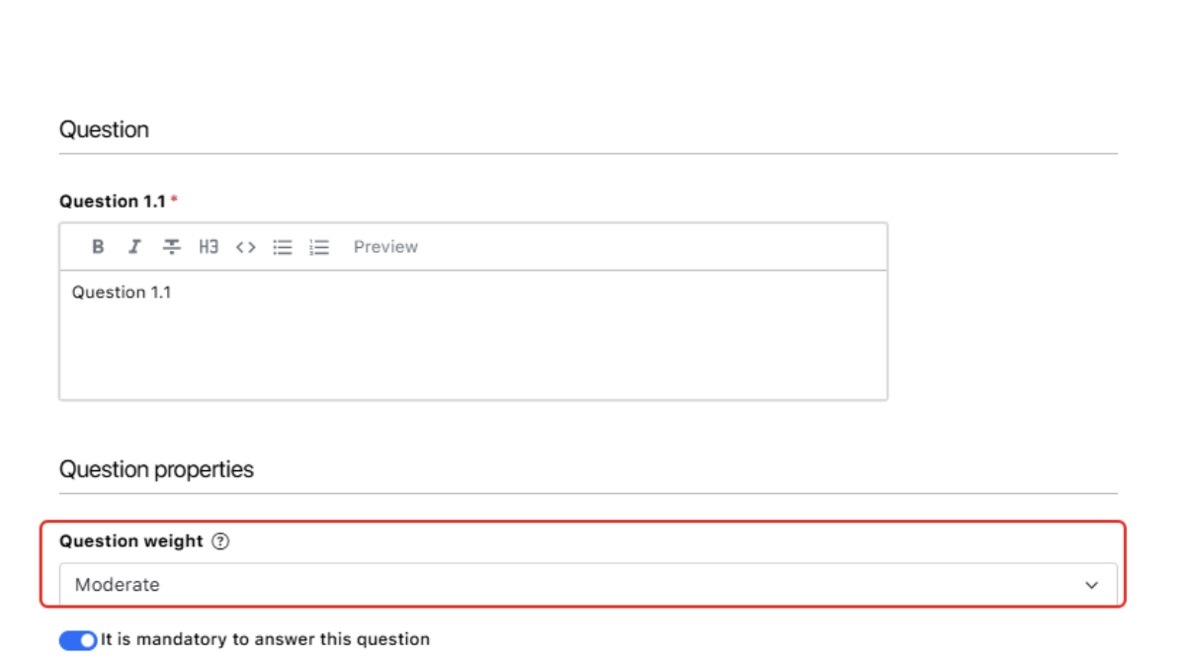
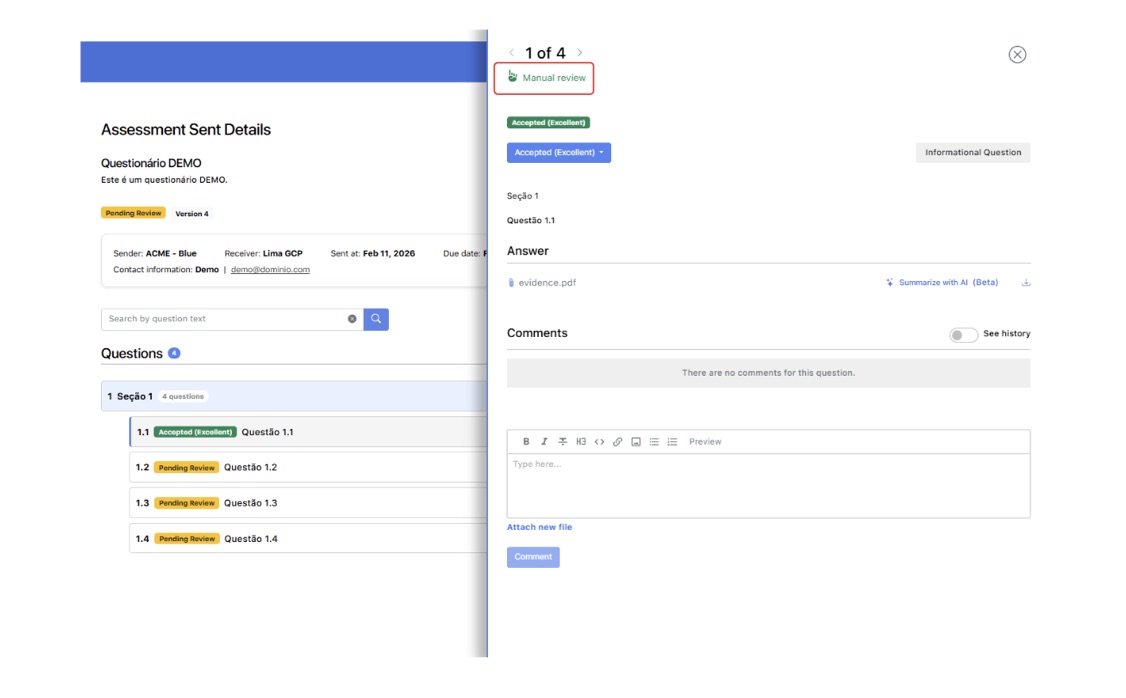
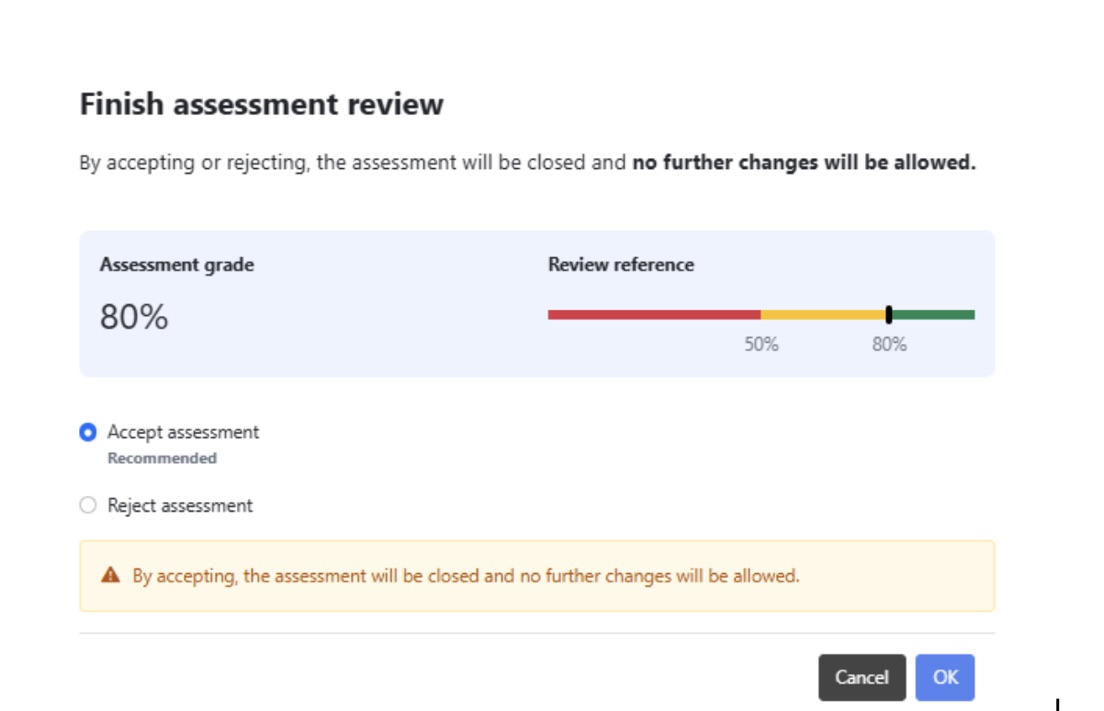
You can now assign specific weights - ranging from Informational to Critical - to individual questions, alongside assigning precise point values to specific answers within your Self-Assessment Questionnaires (SAQs). By doing so, Zanshin takes over the heavy lifting to automatically calculate a final, mathematically sound Assessment Grade. To make this even more powerful, you can set smart approval criteria. This allows the system to instantly evaluate incoming questionnaires against your acceptable risk thresholds and automatically recommend whether to Accept, Reject, or Request Clarification. We have also completely redesigned the reviewer experience. You will find a new, highly intuitive review interface featuring a quick-navigation side panel that keeps all necessary context in one view and auto-advances to the next item, significantly speeding up the evaluation process. Of course, the human element remains vital: reviewers always retain flexible evaluation power to overrule the system's automated recommendations or manually refresh grades on-demand as answers change. Finally, our new partial grading system clearly identifies which complex answers—such as free-text paragraphs or uploaded evidence files—cannot be auto-scored and strictly require human review before a final grade is issued.
Go to the “FOLLOWING” section and select “Questionnaires” on the left-hand menu. Edit a questionnaire you own or create a new one and try the new features.
Here are some screenshots from Zanshin highlighting the new capabilities:
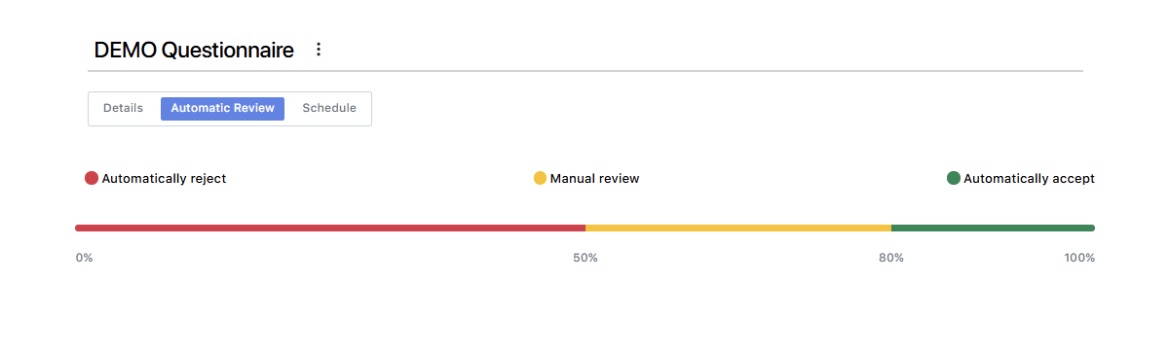
Go to the “FOLLOWING” section and select “Assessments” on the left-hand menu. Open an assessment you just sent that is ready to be reviewed.
Here are some screenshots from Zanshin highlighting the new capabilities:
2. Zanshin Notifications
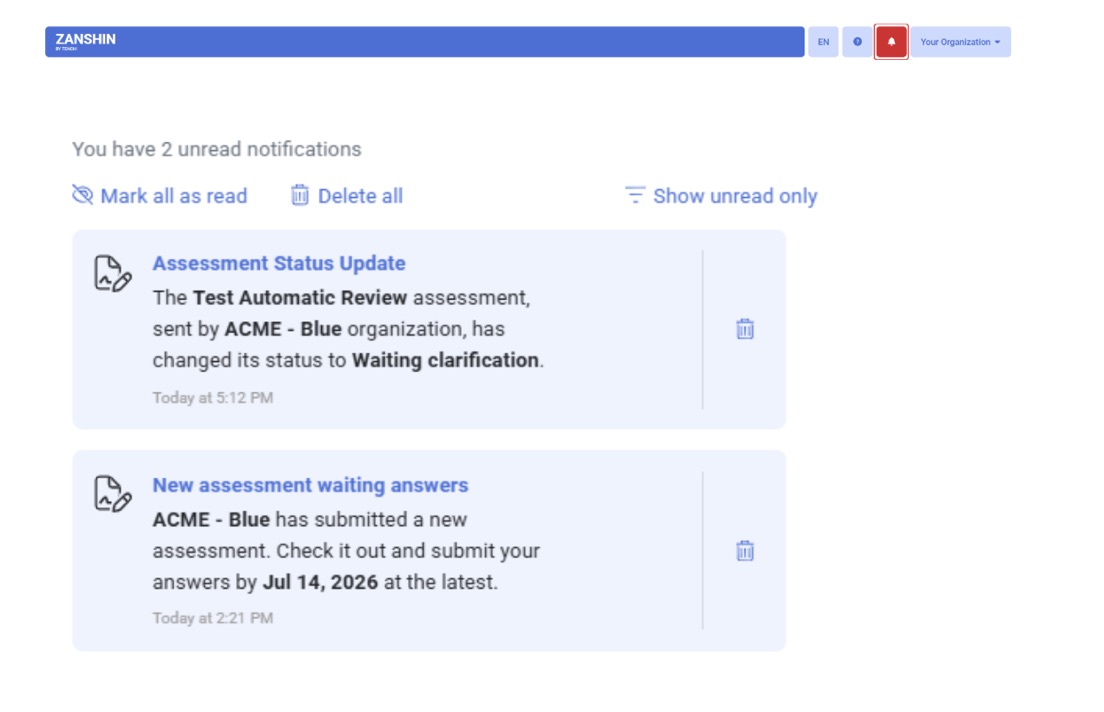
We are also introducing a centralized, secure communication hub. A new "Bell" icon located at the top right of your screen provides an in-platform Notification Center, instantly delivering critical alerts and pending actions directly to you in your preferred platform language. Instead of static text, these action-oriented, clickable notifications act as direct shortcuts, taking you exactly to the specific feature or pending task that requires your immediate attention. To ensure absolute relevance, your notification feed is dynamically tailored to your currently selected Organization and strictly respects your specific Role-Based Access Control (RBAC) permissions, so you only see the alerts that actually matter to your specific role. To help you keep your workspace organized and prioritize your tasks, unread alerts feature a clear visual cue and remain visible for 30 days, while successfully read notifications are neatly retained for 7 days before being cleared.
Here are some screenshots from the Zanshin Notifications feature:
3. Enhanced Third-Party Reports
We have significantly upgraded our Third-Party Reports to provide you with richer, more actionable insights in a highly polished format. To better support our regional users, you can now generate your reports fully in Portuguese. This eliminates language barriers, making it significantly easier and faster to share critical risk insights and findings directly with your local stakeholders and vendors.
Furthermore, we have added a dedicated "Missing Scan Targets" section to the report. This highly visible addition explicitly highlights any relevant environments or scan targets that a third party is currently failing to monitor, immediately exposing critical visibility gaps in your digital supply chain. Your reports also now dynamically support and display key global industry standards, officially adding both ISO 27001 and PCI DSS to the compliance overview so you can easily track vendor adherence.
Finally, we have refined the overall report layout for enhanced clarity and data accuracy. These structural enhancements include adding the exact Date & Time of generation for better version control, updating the default file naming convention for easier file organization, and clarifying the scoring terminology so that it accurately reflects the First Party's specific view of the risk.
4. Organization Profile
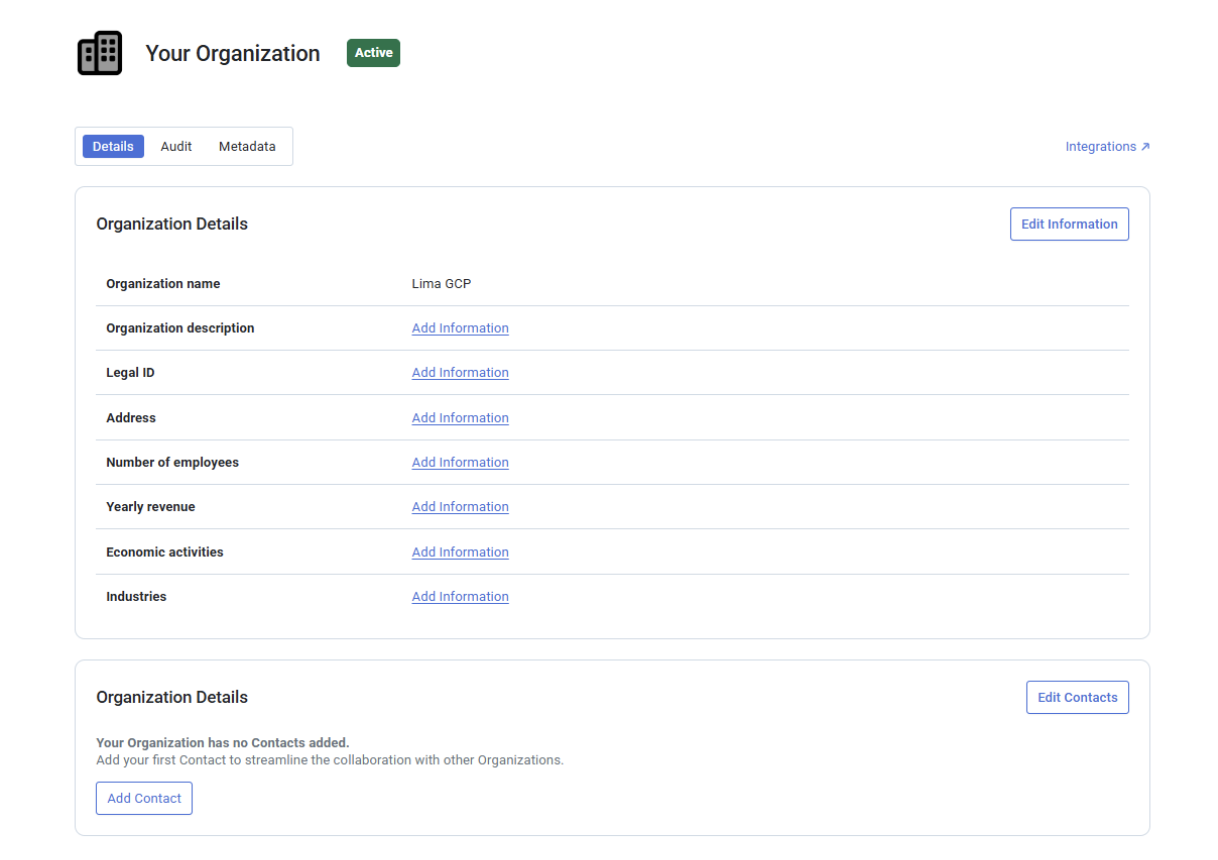
We have upgraded the “Settings” menu to a new, comprehensive “Profile” hub where you can fully manage your organization's structured identity. You can now record vital firmographic data directly within Zanshin, including multiple Legal IDs, exact employee counts, yearly revenue, and NAICS-based industry classifications. To make data entry as seamless as possible, we have also incorporated smart, map-based autocomplete for your address and automated suggestions for your industry codes.
Additionally, we have significantly expanded our contact management capabilities. Moving beyond a single generic contact email, you can now add and manage multiple specific points of contact categorized by department—such as Security, Compliance, or Legal—complete with individual names, emails, and phone numbers.
Go to the “MY ORGANIZATION” section and select “Profile” on the left-hand menu and explore the new “Details” tab.
5. More Accurate Score Calculation
We refined how Alert Severity impacts the overall score, ensuring unresolved Critical and High alerts receive the appropriate weight and cannot be masked by a large number of low-risk resources.
6. New Scan Target Type
Added support for “Zoom Workplace“ expanding the range of platforms and services Zanshin can continuously monitor.
In the “Scan Targets Dashboard“ page, locate the “SaaS” section to find “Zoom Workplace”.
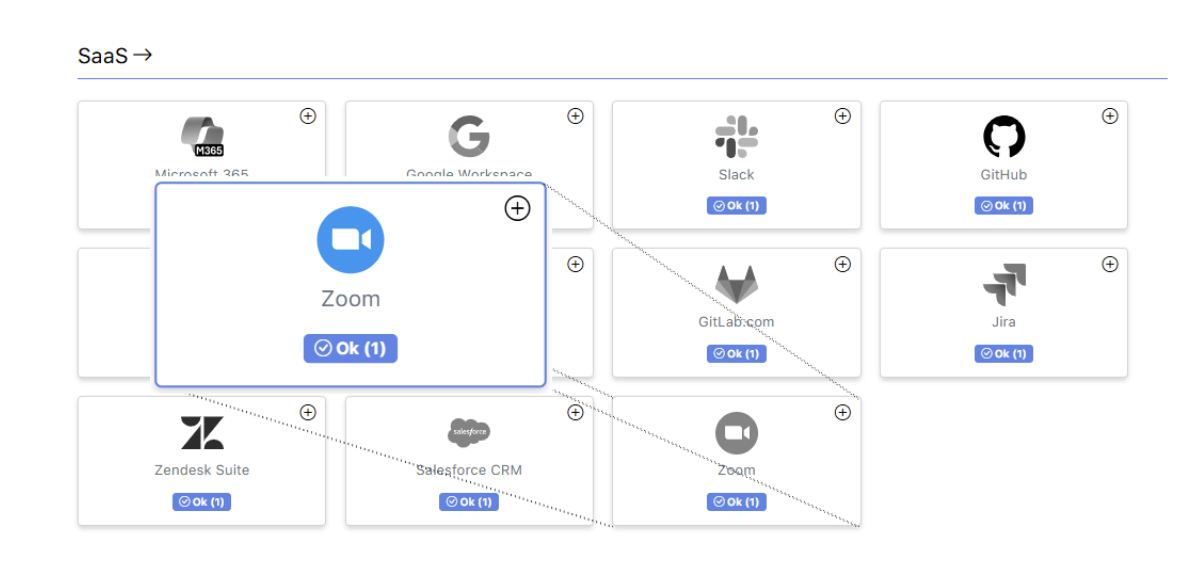
As usual, Zanshin will scan these platforms without ever having access to your sensitive data, such as your organization’s databases data or credentials. We simply ask for the minimal set of permissions to review security-relevant settings, to ensure you stay as safe as possible.
For more information, see: Zoom Workplace - Scan Target Registration.
Zanshin news and updates | May 2026
1. New "My Organization" Dashboard
CISOs and executives now have an aggregated, high-level view of their risks across all monitored scan targets. Instantly assess portfolio health, prioritize critical actions, and efficiently report risk posture to stakeholders. To ensure technical teams still have the granular data they need, the previous dashboard visualizations will be moved to the top of the Alerts page.
Go to the “MY ORGANIZATION” section and select “Dashboard” from the left-hand menu.

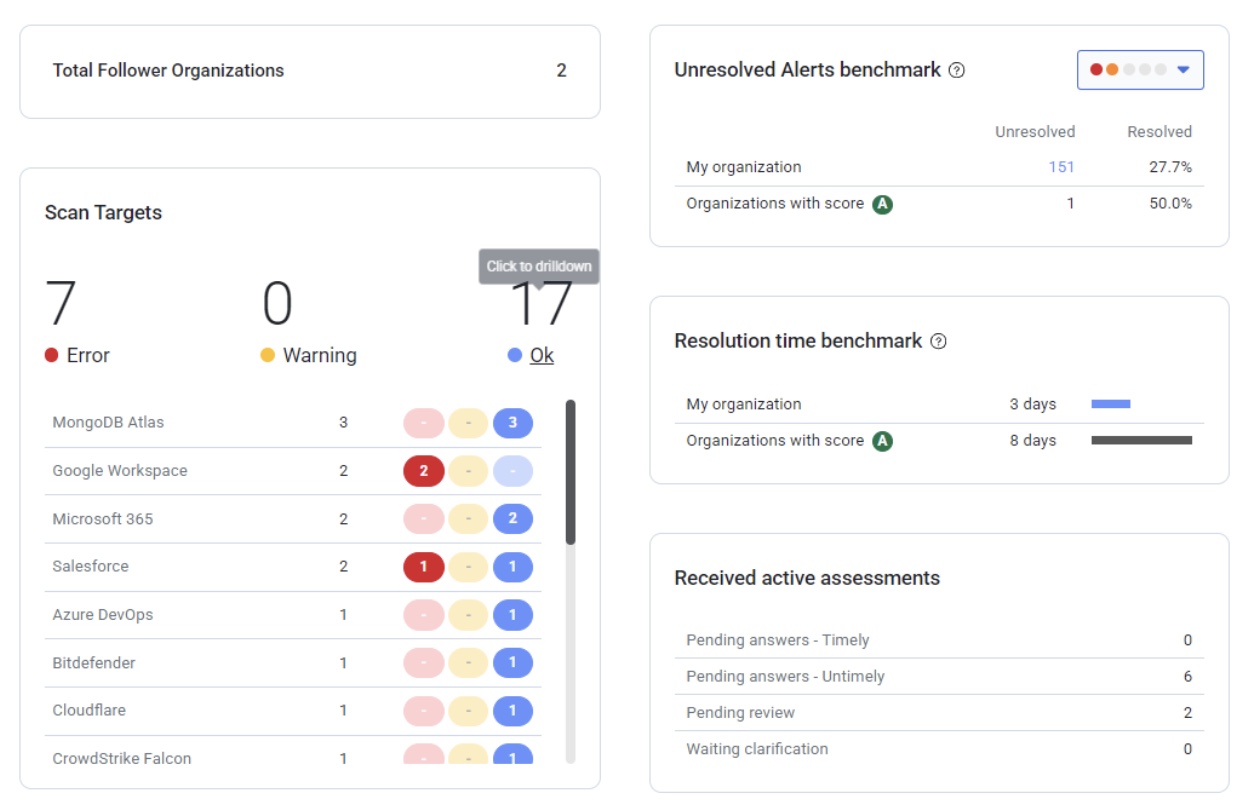
The following elements are presented on the screen above:
- The “All Scan Targets” and “Public Scant Targets” history charts that provide an immediate "at-a-glance" status of the current security health (using the score) while simultaneously showing the stability or volatility of that score over a specific time range .
- A “My Score distribution by Follower Organizations” doughnut chart that shows how the score is distributed by follower organizations.
- A “Compliance” historical line chart that shows how compliance is the organization over a specific time range.
- The number of organizations that are following your organization.
- The “Scan Targets” summary shows the status of the scan targets per technology allowing administrators to instantly identify which specific integrations require immediate attention.
- A “Unresolved Alerts benchmark” table comparing your organization with organizations with “A” score for the selected severities (defaults to critical and high severities).
- A “Resolution time benchmark” table comparing your organization's operational efficiency with organizations with “A” score.
- A “Received active assessments” table showing the number of received assessments by their status helping track the lifecycle of security assessments to ensure that administrative tasks and audits are being completed on schedule.
2. Microsoft 365 Automatic Onboarding
Automating the Microsoft 365 onboarding process is important because it solves the three biggest pain points in technical setups: human error, time drain, and security gaps.
- Elimination of Configuration Errors: Setting up MS365 involves handling sensitive strings like Client IDs, Secret Keys, and Permissions.
- Drastic Reduction in "Time-to-Value": The process is reduced to a few minutes.
- Reduced Support Overhead
- Standardized Security: Least Privilege Principle is enforced. Only request the specific read-only scopes Zanshin needs, preventing users from accidentally granting more access than necessary.
a. Go to the “MY ORGANIZATION” section and select “Scan Targets” from the left-hand menu and click the “+” button in the “Microsoft 365” box.
b. Follow the instructions in the onboard process until you reach step 4.
c. In step 4 you will be instructed to onboard it automatically. Just follow the instructions. If you want to proceed manually due to security policies in place at your organization please execute the steps in Integrating Microsoft 365 through admin console.
3. New Scan Target Types
Added support for Azure DevOps and JumpCloud Open Directory Platform, expanding the range of platforms and services Zanshin can continuously monitor.
In the Scan Targets Dashboard page, locate the “SaaS” section to find “Azure DevOps” and the “Identity and Access Management” section for “JumpCloud Open Directory Platform”.
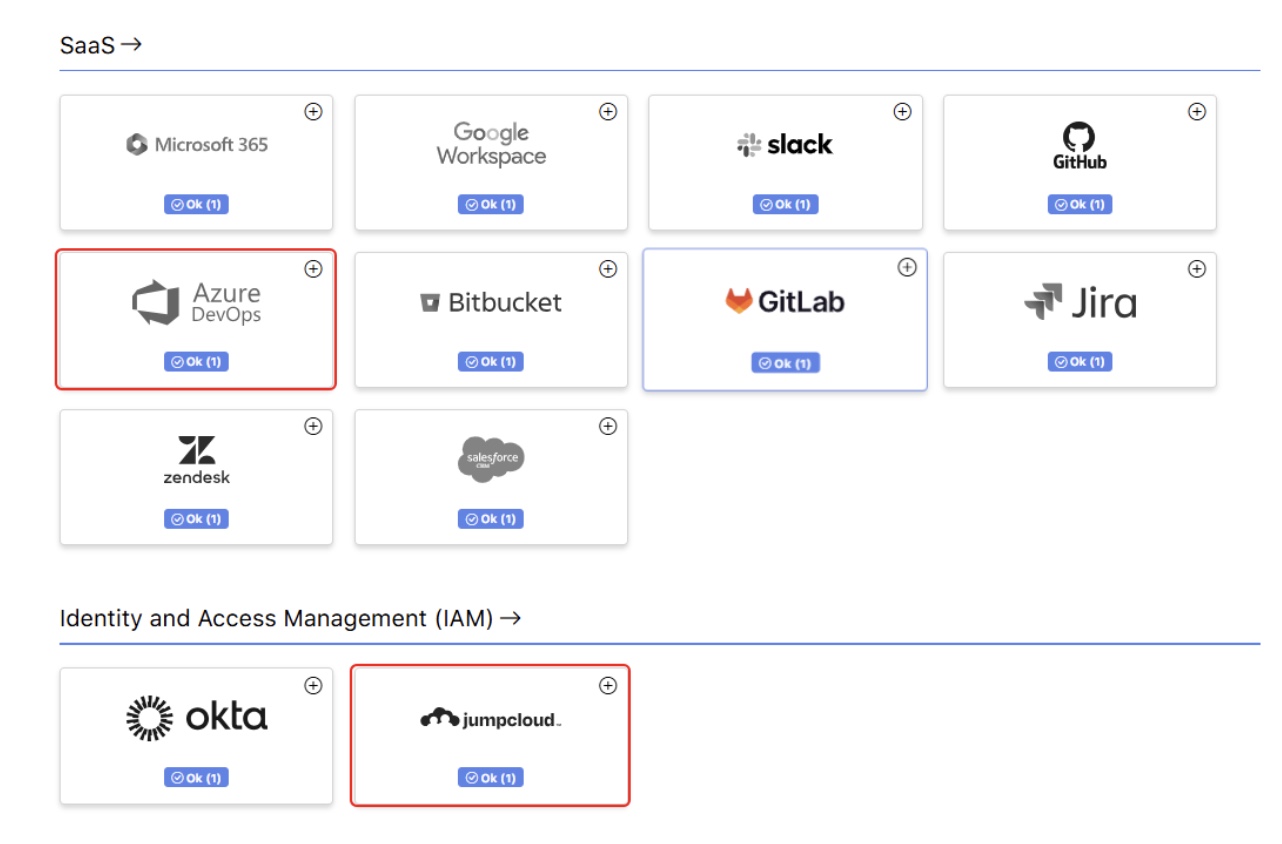
As usual, Zanshin will scan these platforms without ever having access to your sensitive data, such as your organization’s databases data or credentials. We simply ask for the minimal set of permissions to review security-relevant settings, to ensure you stay as safe as possible.
For more information, see: Azure DevOps Scan Target Registration on Zanshin and JumpCloud Open Directory Platform Registration in Zanshin.
4. Auto-Detect and Unshared Scan Targets
Transparency is key to a secure supply chain. If Zanshin detects that you possess relevant scan targets that you have not onboarded or explicitly shared with your followers, the platform will alert you.
- Navigate to the "MY ORGANIZATION" section in the left-hand vertical menu and select "Scan Targets".
- Select the "Dashboard" or "List" tab. In both you will find the "Recommendations" section at the top of the screen, as shown below.
- For scan targets not shared with all followers, you will see the recommendation below.
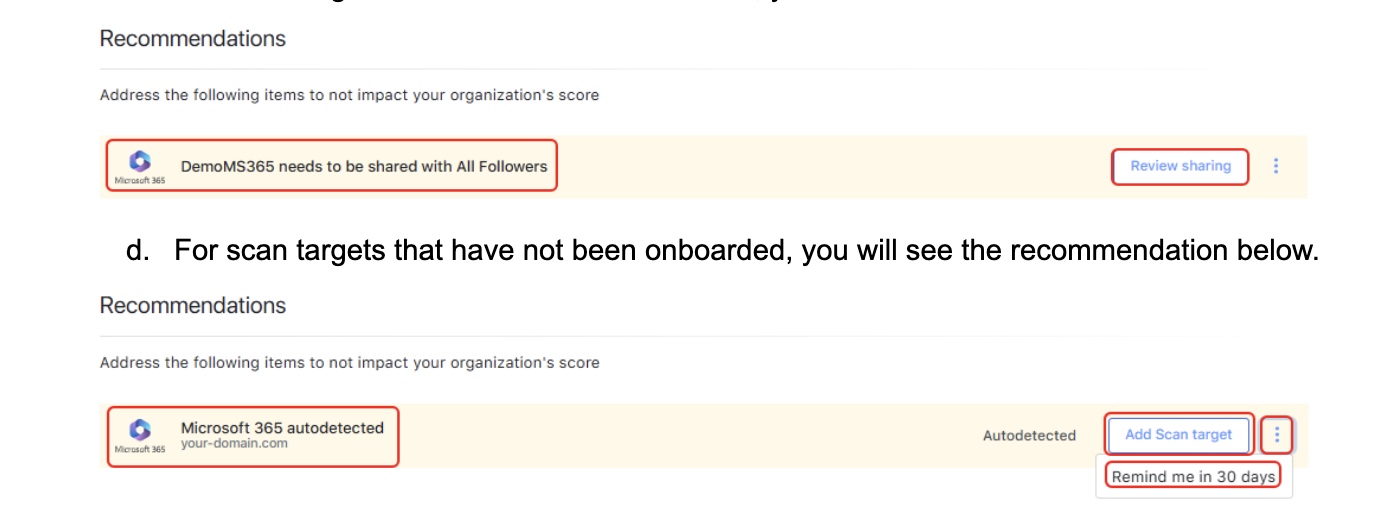
For more information, see: Understanding Automated Scan Target Detection.
Zanshin news | February 2026
1. New Following Dashboard
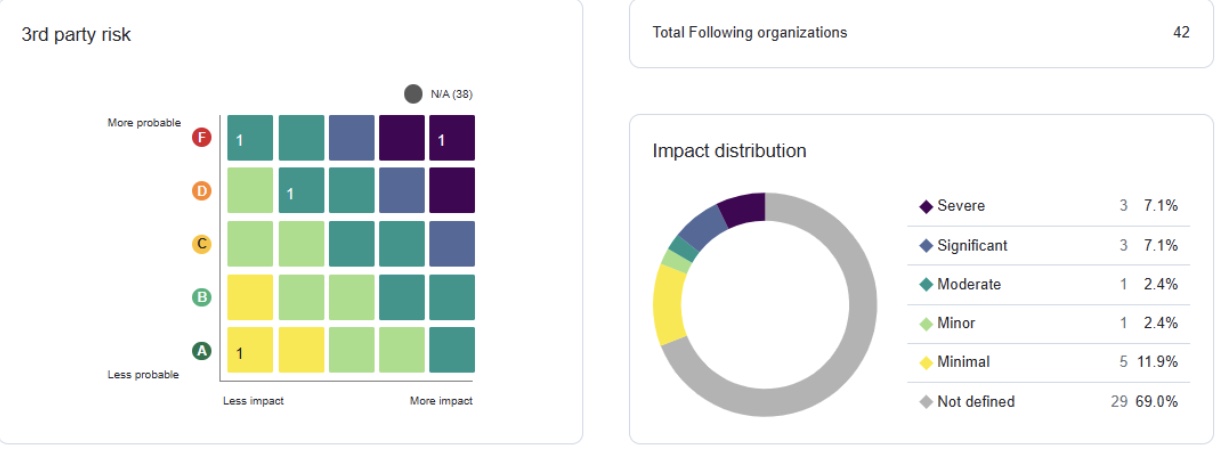
CISOs and executives now have an aggregated, high-level view of third-party risk across all monitored vendors. Instantly assess portfolio health, prioritize critical actions, and efficiently report risk posture to stakeholders.
Go to the “FOLLOWING” section and select “Dashboard” from the left-hand menu.
The following elements are presented on this screen:
- The “3rd party risk chart (Risk Matrix)” is based on two primary dimensions: Business Impact and Probable/Likelihood determined by the measured score. Each quadrant displays the number of third parties within that specific score/impact level.
- A “Impact distribution” doughnut chart that shows the count and percentage of following organizations falling into each of business impact levels.
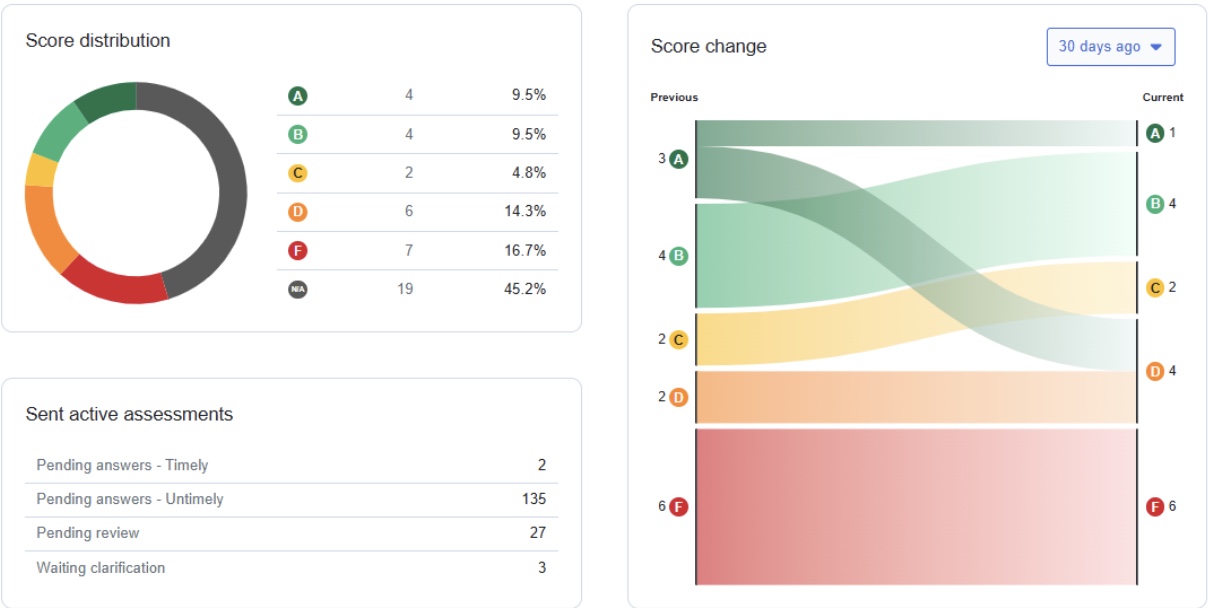
- A “Score distribution” doughnut chart that shows the count and percentage of following organizations falling into each of the score grades.
- A “Score change” Sankey Diagram that shows the change in score grades for the organizations being followed over a period.
The “Sent active assessments” summary that shows the assessments sent to “Following Organizations”, categorized by status.
2. AI Summary for SAQ
The AI-Powered Summary for SAQs transforms the way your team reviews assessments. By automating the analysis of documents submitted by third parties, it significantly accelerates the assessment process and drastically reduces the manual effort required to review supporting evidence.
Greater efficiency. Greater accuracy. Far less time spent on operational analysis.
How to access:
a. Go to the “FOLLOWING” section and select “Assessments” from the left-hand menu.
b. Identify the assessments that are in a pending review status.
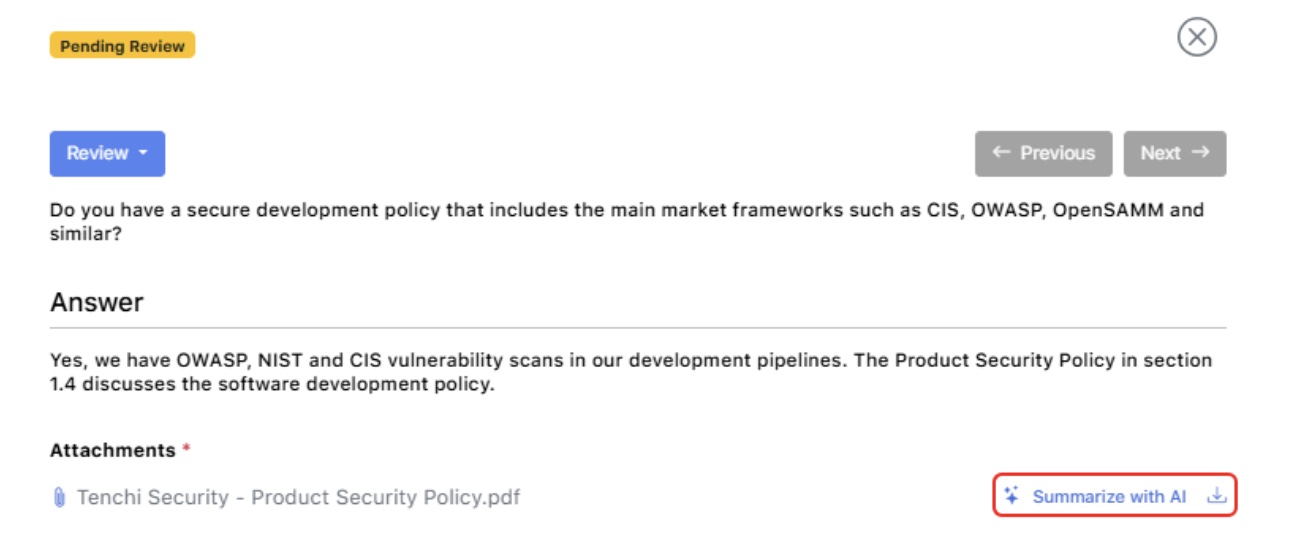
c. When reviewing a question that includes or requires an attachment, click "Summarize with AI"**
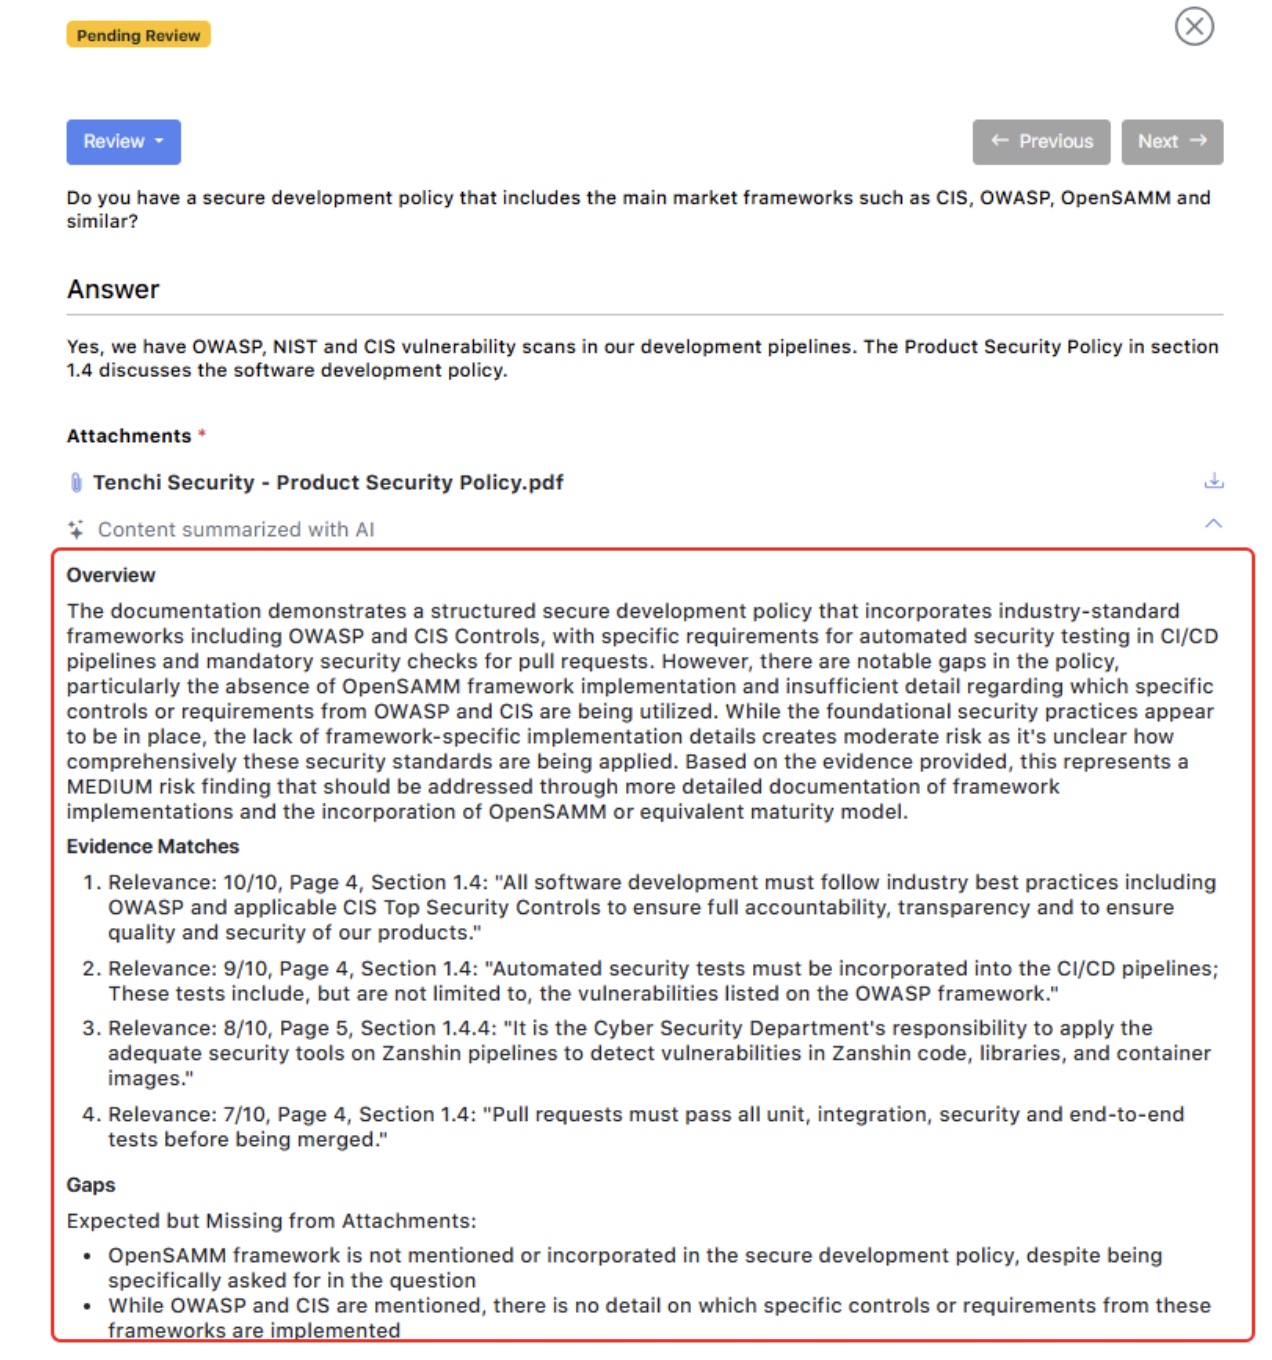
d. The feature performs a deep evidence analysis by pinpointing relevant matches within your files and identifying specific documentation gaps to ensure all requirements are met.
** at the moment only pdf files can be summarized
3. New Scan Target Types
Added support for Okta and Sophos Endpoint, expanding the range of platforms and services Zanshin can continuously monitor.
Check the “Identity and Access Management (IAM)” section in the Scan Targets Dashboard page for the “Okta Workforce Identity” box and the “Security Tools” section for the “Sophos Endpoint” box.
As usual, Zanshin will scan these platforms without ever having access to your sensitive data, such as your organization’s databases data or credentials. We simply ask for the minimal set of permissions to review security-relevant settings, to ensure you stay as safe as possible.
4. Enhanced Compliance Reporting
Zanshin now supports compliance reporting against PCI DSS v4.0.1 for your organization and for the organizations you are following, helping you meet the latest industry standards.
How to access:
- In the “MY ORGANIZATION” or “FOLLOWING” sections, select “Compliance” from the left-hand menu.
- The compliance dashboard will open, displaying the available frameworks. Selecting PCI DSS allows you to navigate through its specific compliance requirements.

5. Third-Party Public Score
Organizations can quickly assess third-party baseline security posture and better prioritize monitoring, due diligence, and engagement. This eliminates a gap in risk evaluation, particularly during early-stage monitoring, where only public data is available.
How to access:
a. In the “FOLLOWING” section, select “Organizations” from the left-hand menu.
b. In the “Following Organizations List”, click on the following organization you want to view its details, as shown below.
c. In the organization’s details page click in the “Dashboard” tab, as shown below. Two charts are displayed showing:
- The historical following organization score considering all their scan targets.
- The historical following organization score considering their public scan targets only.


The New Security Score: Moving Beyond Relative Risk | November, 2025
Security ratings are essential for managing risk and they are most valuable when providing enhanced transparency and stability, with metrics directly linked to action.
Our data science team is taking advantage of the rapid growth of the Zanshin solution, which brings more volume and variety to our dataset. Based on this work, we are excited to announce an upgrade to our scoring methodology, ensuring it more accurately represents the security posture of organizations.
What changed?
- A simplification of the factors used to calculate scores, and a calibration of their relative weights;
- Adjustments to parts of the score calculation which were evaluating organizations relative to the entire population in our platform. This means your score is now based solely on your own security performance, allowing you to set confident security goals.
The New Security Score is a monumental step toward providing a security rating that is not just a benchmark, but a trusted and transparent tool for improving your risk posture.
The Absolute Security Score: Moving Beyond Relative Risk | November, 2025
Security ratings are essential for managing risk, but they are most valuable when transparent, stable, and directly linked to action.
We are excited to announce a fundamental upgrade to our scoring methodology, transitioning from a relative system to a clear, absolute scoring model that provides greater transparency and predictability to our customers.
Why the change?
- Current Scores: Under the relative system, your score was dependent on the performance of all other organizations. If your peers significantly improved their security, your score could drop—even if your own security posture remained unchanged.
- New Scores: The Absolute Security Score ties changes exclusively to your organization's actions. You only move up or down when your security posture genuinely improves or declines. Your score is now based solely on your own performance, allowing you to set confident security goals.
The new Absolute Security Score is a monumental step toward providing a security rating that is not just a benchmark, but a trusted and transparent tool for improving your risk posture.
Latest Product Updates | October, 2025
1. Role-Based Access Control (RBAC)
This concept enhances access management by allowing organizations to assign specific roles with predefined permissions to users. This ensures that users only have access to relevant sections in Zanshin, reducing security risks and improving operational efficiency.
To access this feature:
1. Go to the “MY ORGANIZATION” section and select “Members” from the left-hand menu.
2. Click on the “Roles” tab.
3. Here you can see the roles you created and the predefined roles (labeled in blue) that come with Zanshin.
Please see a sample:

Customized roles can be created by assigning the required permissions and users to them, aligning with your specific business needs.

2. New Scan Target Types
Added support for SentinelOne Singularity and Microsoft Intune (under Microsoft 365), expanding the platforms and services Zanshin can continuously monitor. Check the “SaaS” section in the Scan Targets Dashboard page for the “Microsoft 365” box and the “Security Tools” section for the “SentinelOne Singularity” box.

As usual, Zanshin will scan these platforms without ever having access to your sensitive data, such as your organization’s databases data or credentials. We simply ask for the minimal set of permissions to review security-relevant settings, to ensure you stay as safe as possible.
Note: Current Microsoft 365 customers being monitored by Zanshin could experience an impact on their organization score if they use Microsoft Intune.
3. Assign Business Impact to 3rd Parties
This feature allows first-party users (typically TPCRM Managers) to assign a Business Impact level to each of their third-parties. The assigned impact level reflects how critical a third party is to the organization's operations and helps prioritize risk management activities. Business impact values can be set individually or in bulk, and can be used as filters across key views such as the Following Organizations List and 1st Party Portfolio Management Dashboard.
In the “FOLLOWING” section, select “Organizations” from the left-hand menu.
The Following Organizations List will appear.
Check each following organization and choose the desired Business Impact level to set from the dropdown menu above it.
See the sample below:
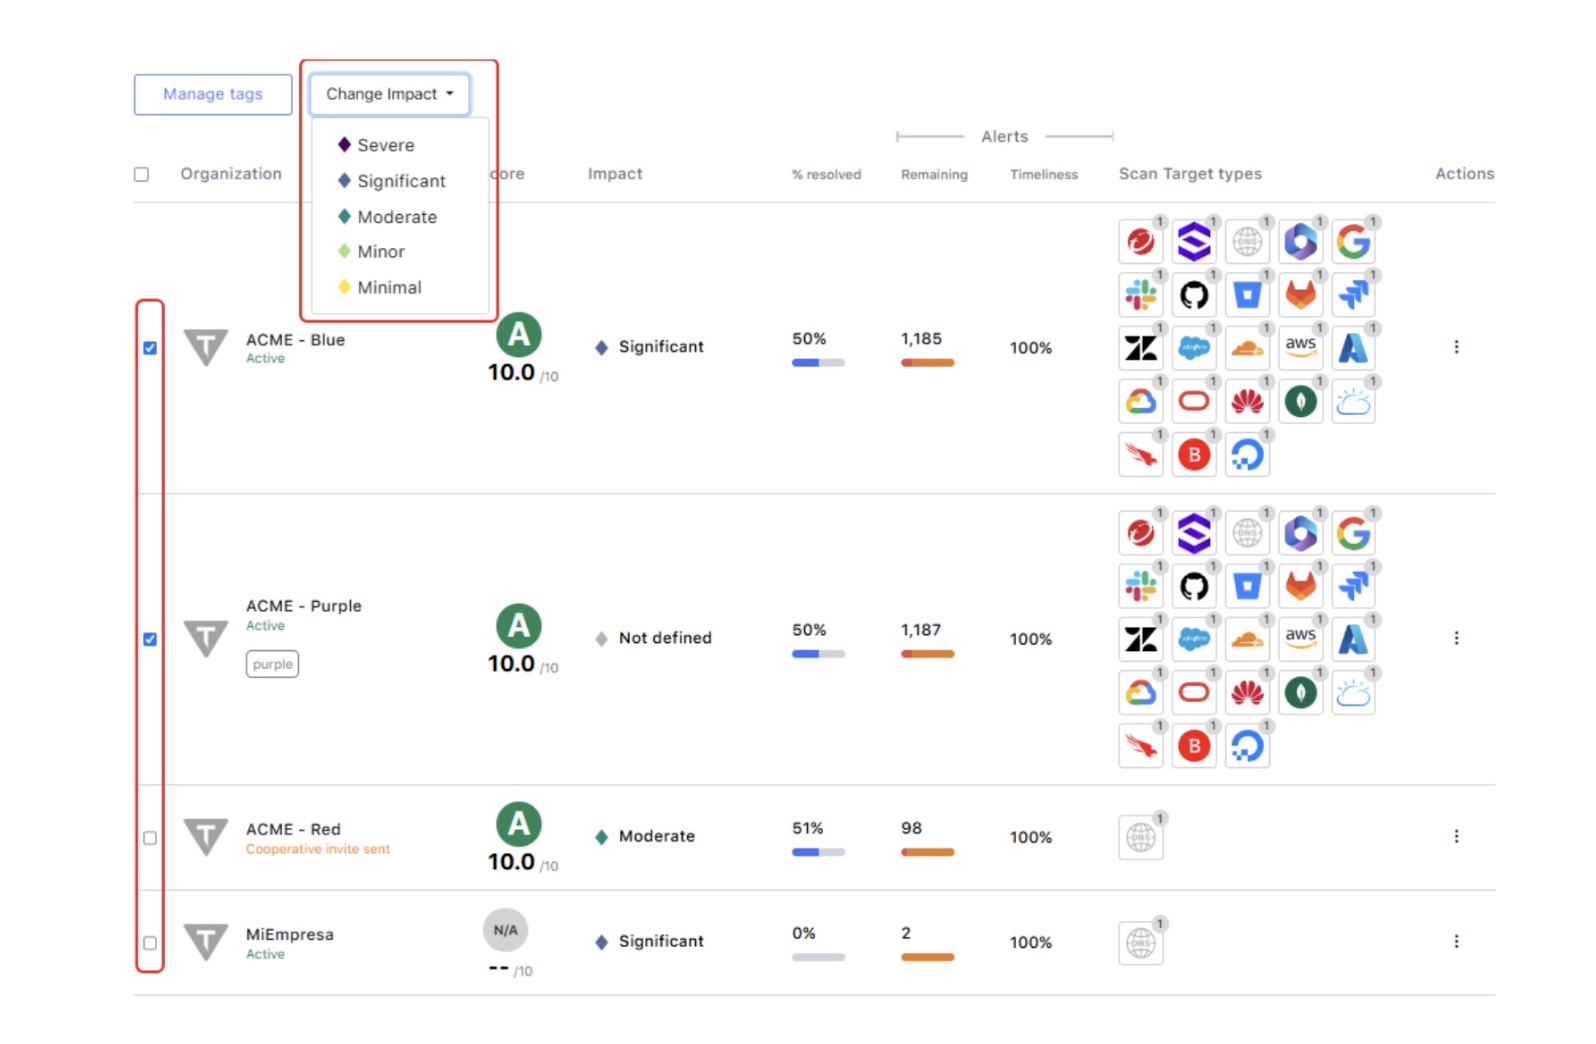
This classification will also be available during onboarding (Pre-Contract Due Diligence), on the Following Organization profile, and within the Following Organizations List for easy management and visibility.
4. New Reports (Third Party and Self-Assessment)
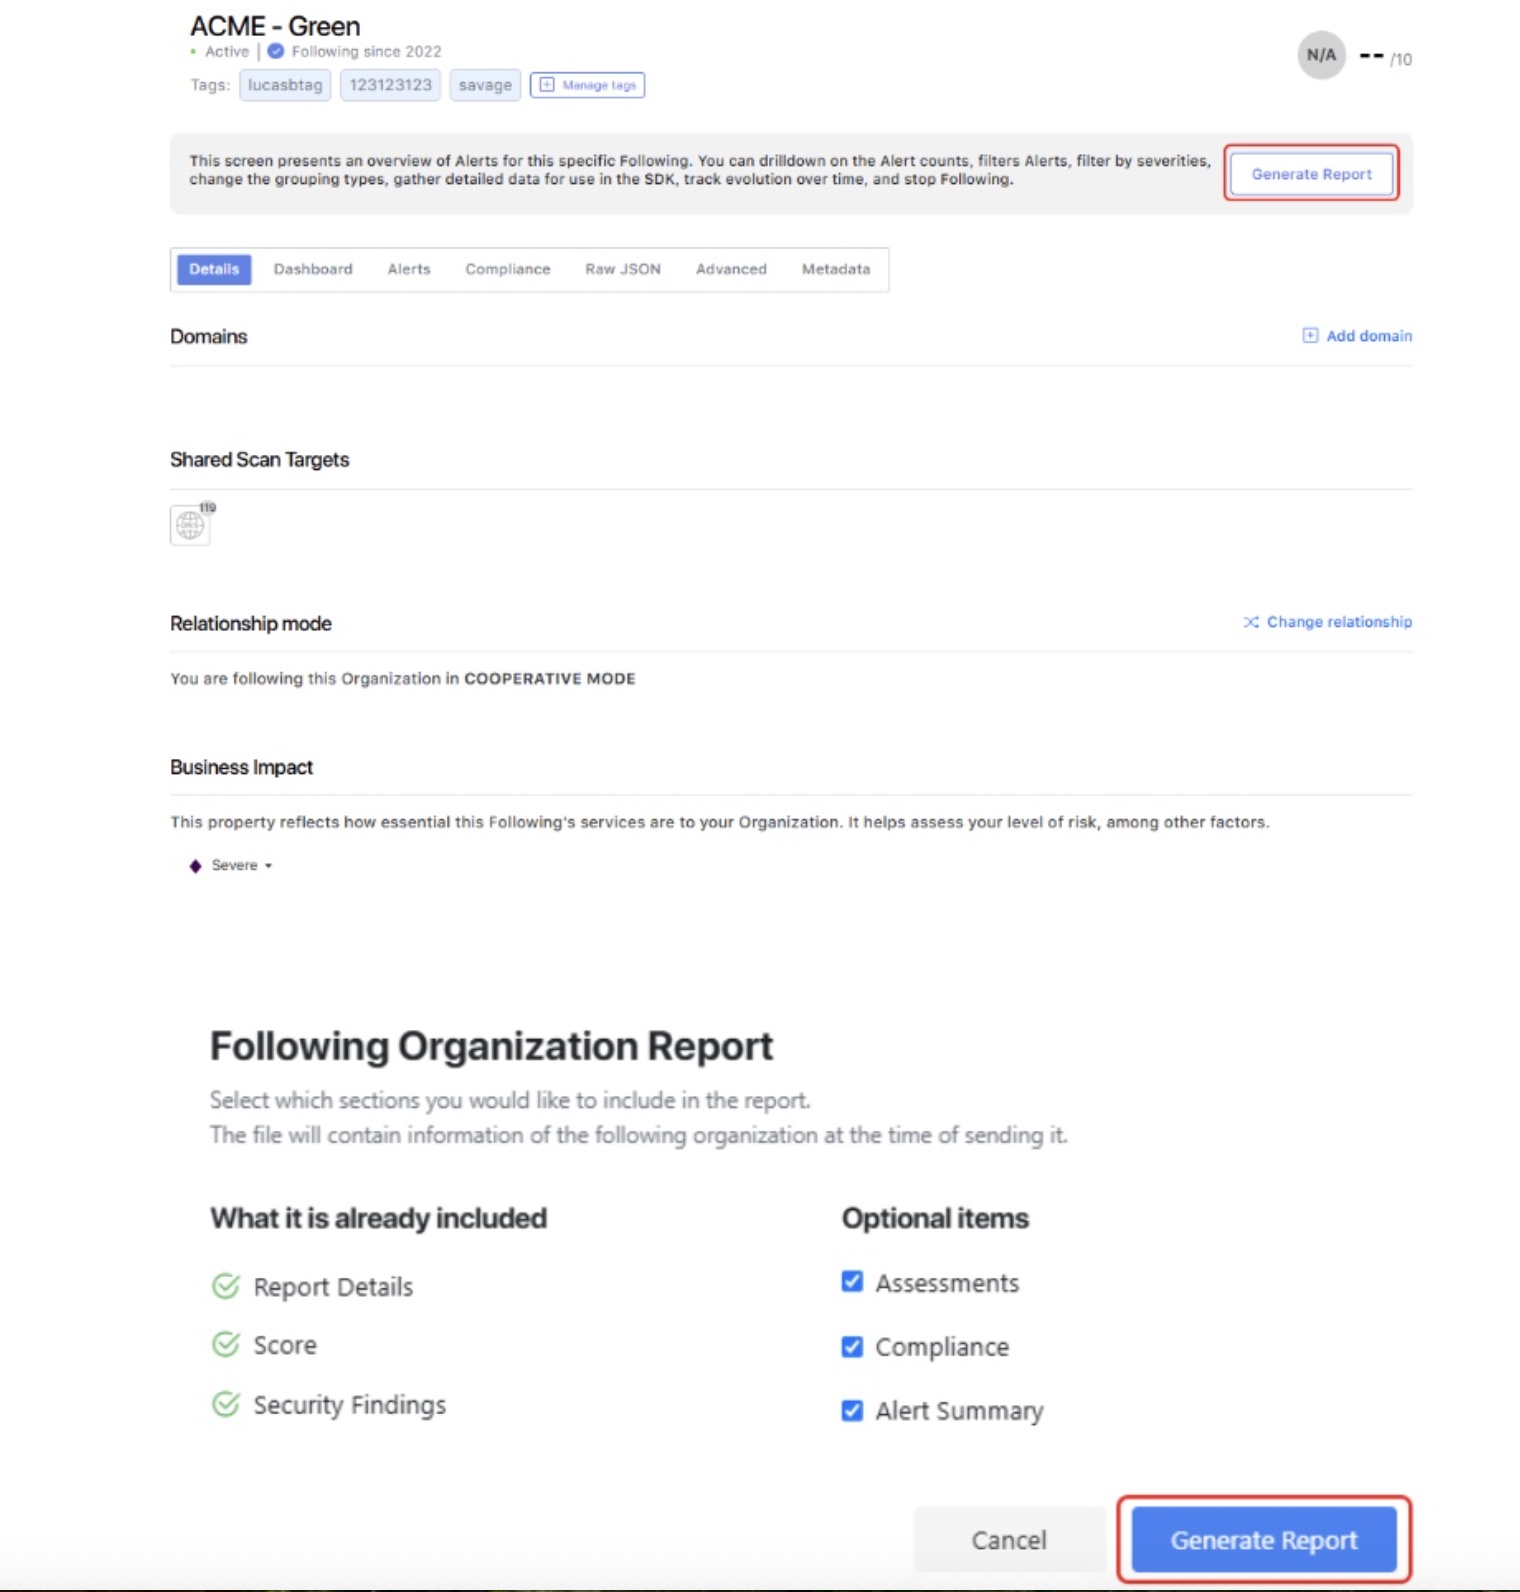
For third-party reports, go to the “FOLLOWING” section, and click on “Organizations”. In the Following Organizations List, select the one to generate the report for by clicking on it. Click on the “Generate Report” button and select the appropriate options.
Here is a sample:
For self-assessment reports, go to the “FOLLOWERS” or “FOLLOWING” section and click on “Assessments”. Click on the questionnaire you want to generate the report for, and click on the “Self-Assessment Report” button that should appear.
Here is a sample:

5. (SAQ) Historical Information
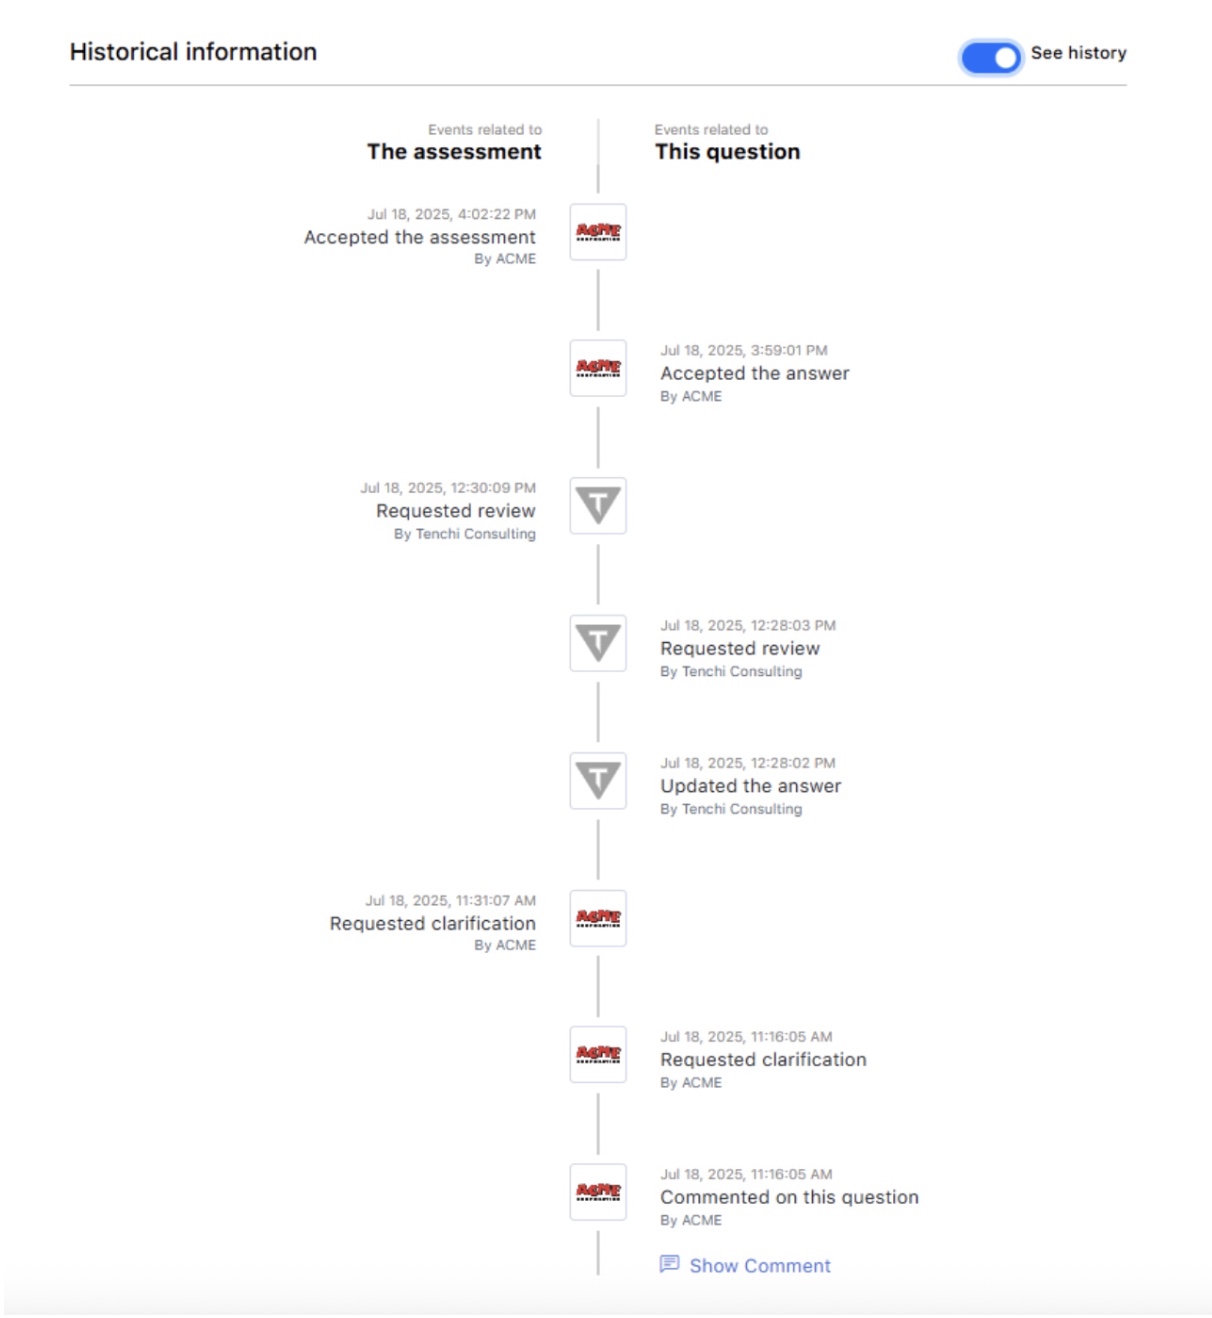
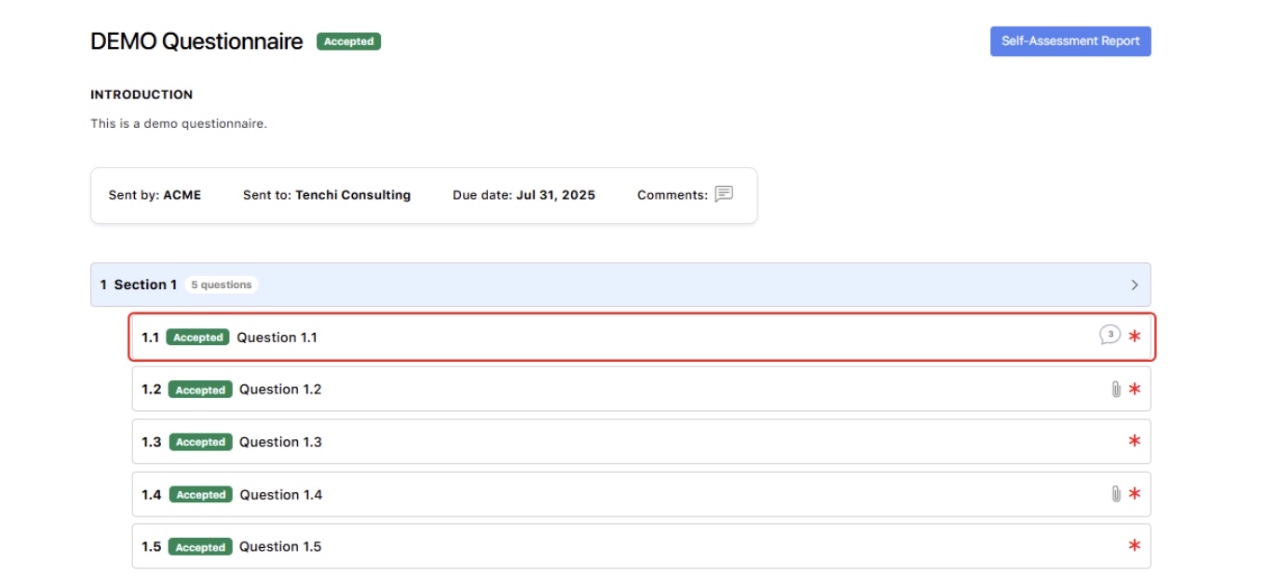
This feature allows users to view the complete historical information for an assessment, including detailed information for each question (such as the answers and comments provided), any associated comments for the questionnaire, the users that provided information, and the history of status changes. It aims to enhance transparency and traceability within assessments and the interaction between organizations (1st party and 3rd parties).
Questionnaire level historical information sample:
Go to the “FOLLOWERS” or “FOLLOWING” section and click on “Assessments”. Click on the questionnaire to check the historical information, and click on the “Comments” icon.
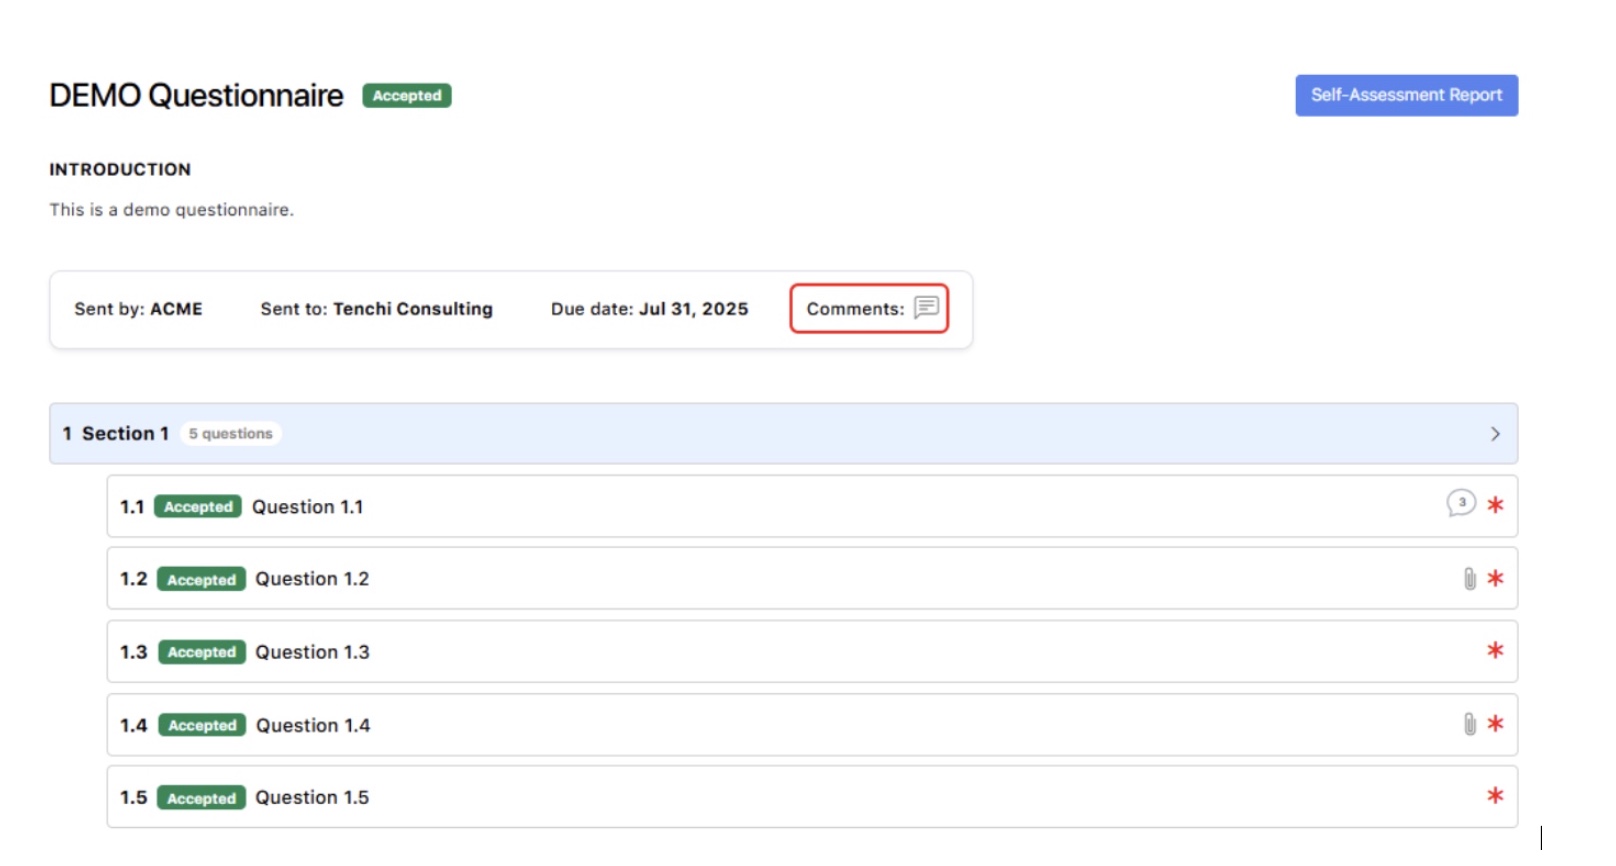
Toggle "See history" on.
Question level historical information sample:
Go to the “FOLLOWERS” or “FOLLOWING” section and click on “Assessments”. Click on the questionnaire to check the historical information, and click on the desired question.
Our Customer Success team is always ready to assist you in case you have any questions.
Latest Enhancements and Updates | September/25
Here at Tenchi Security, we’ve been working hard to make Zanshin more powerful, accurate, and aligned with your needs. Here’s a look at the latest features we’ve added over the past months to help you reduce risk, stay compliant, and work more efficiently.
🔎 Summary of Updates
Security Score Enhancements:
Historical score performance: now you can analyze historical score records up to 12 months.
New score based exclusively on public scan target information, so that 3rd parties security diligence on the specific topic of public attack surface security can be examined
Expanded Coverage: New scan target types - Digital Ocean and Trend Micro Vision One.
Compliance Reporting Upgrade: Support for CIS Controls 8.1, NIST CSF v2.0, and ISO 27001:2022.
Improved Scan Accuracy: Better severity ratings and precision for domain scans.
Faster Workflows: Bulk tagging for scan targets and unlimited bulk execution of alert tasks.
⚠️ Deprecation Notice: Some API endpoints are already deprecated and will be removed on September 22, 2025
-
💡 Why it matters
These updates bring:
More visibility into the security posture over time.
Broader risk coverage with additional platforms supported.
Stronger compliance alignment to meet evolving regulatory demands.
Sharper insights with more accurate scan results.
Greater efficiency to save time managing alerts and scan targets at scale.
Clear transition time to move away from deprecated API endpoints before removal.
Zanshin evolves alongside you - giving you the clarity to spend less energy chasing risks and more time managing them with confidence.
👉 Watch the video below to see Zanshin’s updates in action - or click through to our website for all the details.
Pre-Contract Due Dilligence
We're excited to announce the launch of our Pre-Contract Due Diligence feature, designed to significantly enhance your ability to assess third-party security. With this new capability, Zanshin users can evaluate a vendor’s posture either through continuous monitoring or a one-time assessment - streamlining both onboarding and ongoing oversight by automating data collection and analysis.
Why It Matters:
Proactive Risk Reduction: Identify vulnerabilities before formal agreements, ensuring stronger security from day one.
Streamlined Workflows: Automated data gathering replaces manual spreadsheets, saving time and reducing human error.
Flexible Monitoring: Choose between a one-time due diligence check or continuous oversight based on your risk profile.
Full Visibility: Combine inside-out and outside-in assessments to get a comprehensive view of third-party security.
How It Works
Search or Create: Enter a third party’s domain or name; if it doesn’t exist, create a new organization.
Configure Domains: Add one or more domains for the third party you’re assessing.
- Select Relationship Mode:
- Anonymous Mode:
- Third party is unaware of the monitoring.
- Cooperative Mode:
- Third party consents to share data.
Assign Tags: Categorize and group organizations internally for easy filtering.
Review & Confirm: Verify selected third party, domains, relationship type, and tags—then save.
View Score: Within six hours, Zanshin will display the initial security score; updates occur every six hours.
Watch the short teaser below.
Updates | May, 2025
Exciting new features that will significantly enhance our product's capabilities have been released:
- Scan Targets sharing settings
- Domain Scan Targets visibility
Crowdstrike Falcon and Microsoft Defender for Endpoint scanning support
New filters in Dashboards and Alerts Lists
Zanshin rule detection improvements
Navigation to Alerts is now restored
Scan Targets sharing settings
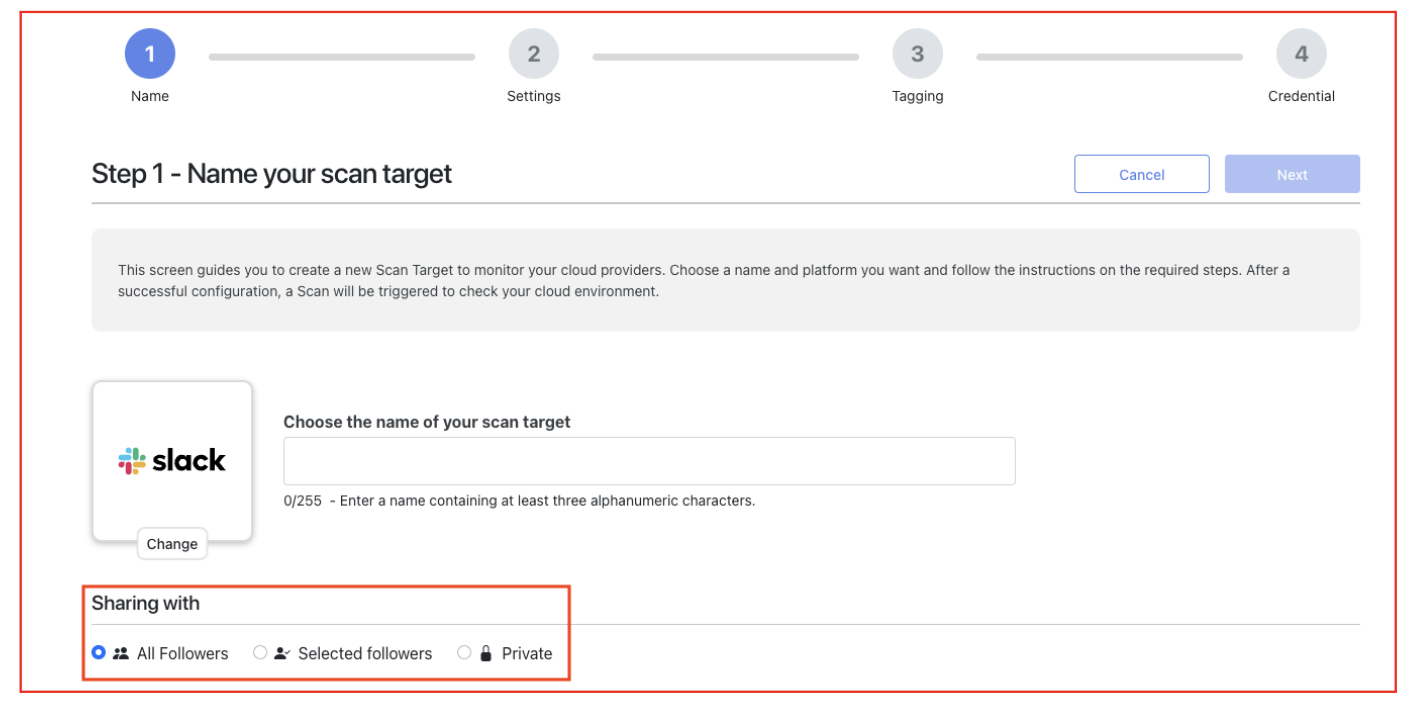
Now, each third-party organization (Following Organization) will be able to define which Scan Targets they share with which first-party organization (Follower Organization). This applies in several places in Zanshin:
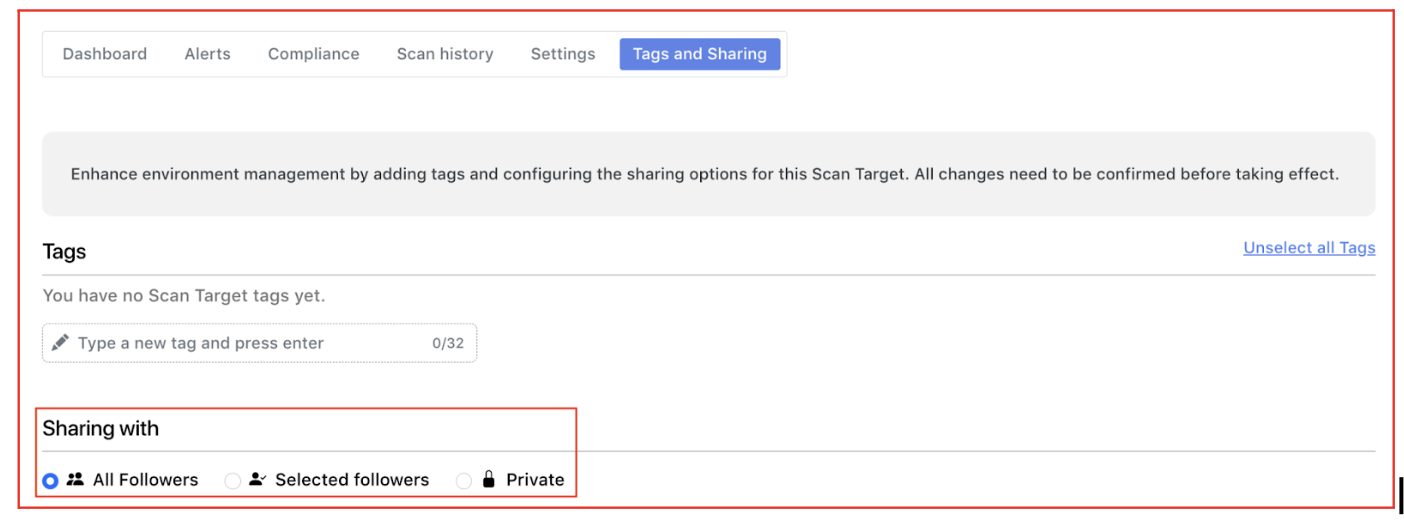
- During the creation of a new Scan Target, a sharing configuration allows to select the appropriate sharing type:
- All Followers: The Scan Target being created will be visible to all Follower Organizations.Selected followers: Only some of the Follower Organizations will have visibility on the Scan Target being created.Private: There is no Follower Organization with visibility on the Scan Target being created.
On the Scan Target details page, the Following Organization will be able to see the Tab “Tags and Sharing”, in order to view or edit the sharing type and the list of Follower Organizations that will have visibility on the corresponding Scan Target.
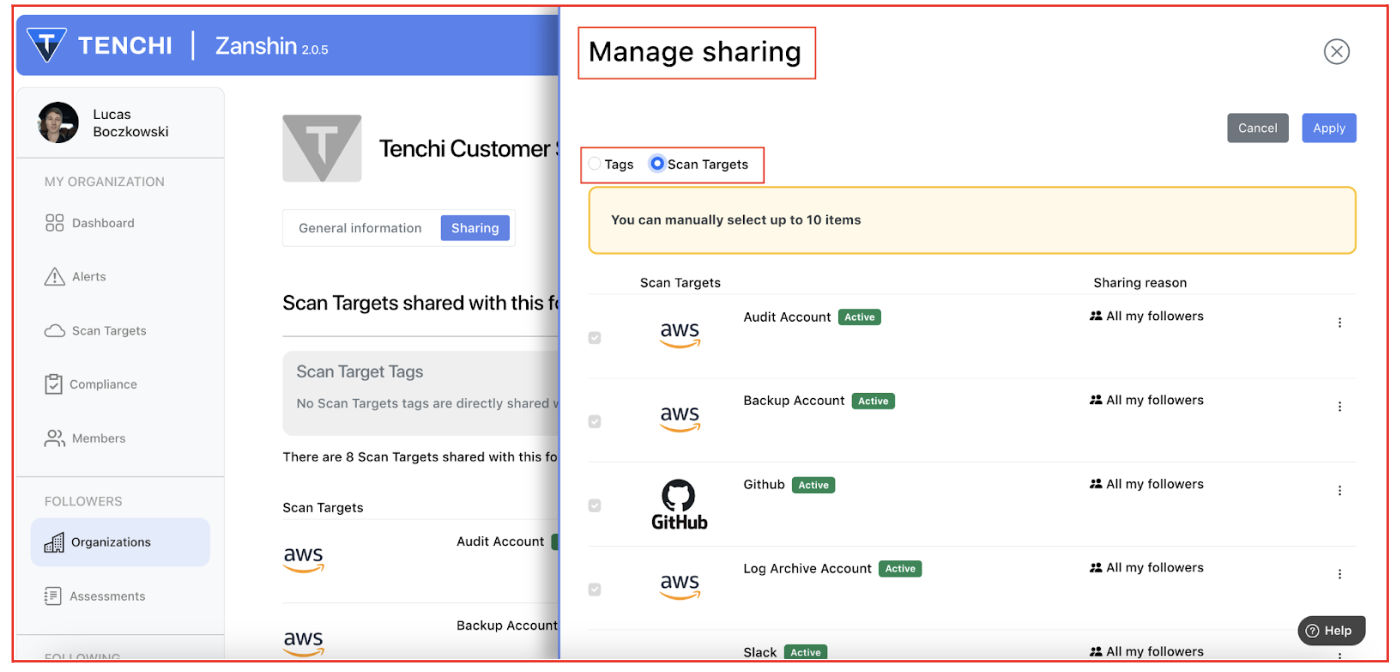
In the Follower Details page, the Following Organization is now able to select (by Scan Target Tag and Scan Target Name) the Scan Targets needed to be shared with the corresponding Follower Organization.
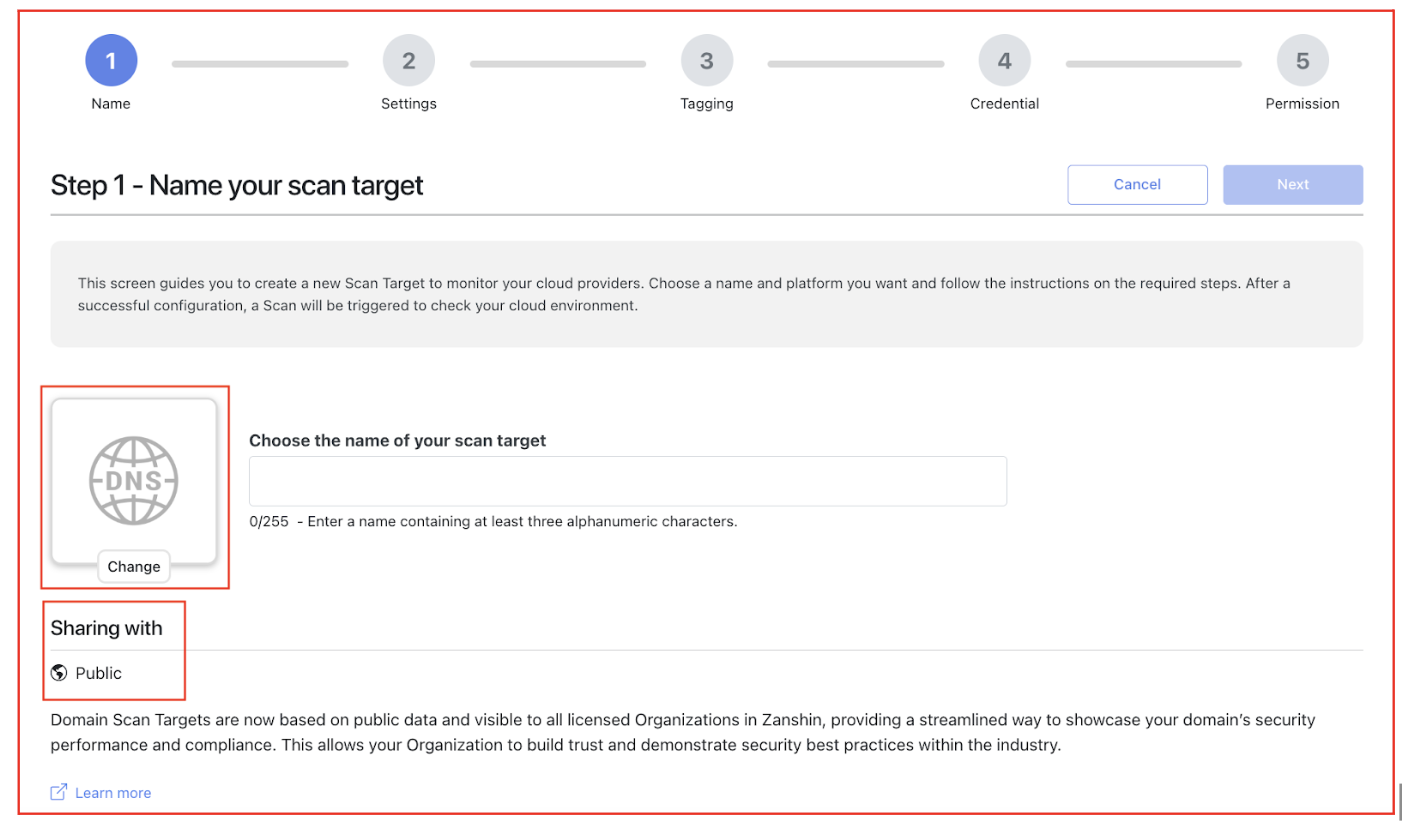
Domain Scan Targets visibility
Since the findings related to Domain Scan Targets are based on public data, they will now be visible to all licensed Organizations in Zanshin. This will provide a more streamlined way to showcase your domain’s security performance and compliance, and bring Zanshin in line with widespread industry practice. This allows your Organization to build trust and demonstrate security best practices to your customers and partners.
Crowdstrike Falcon and Microsoft Defender for Endpoint scanning support
Zanshin now supports scanning two additional platform types:
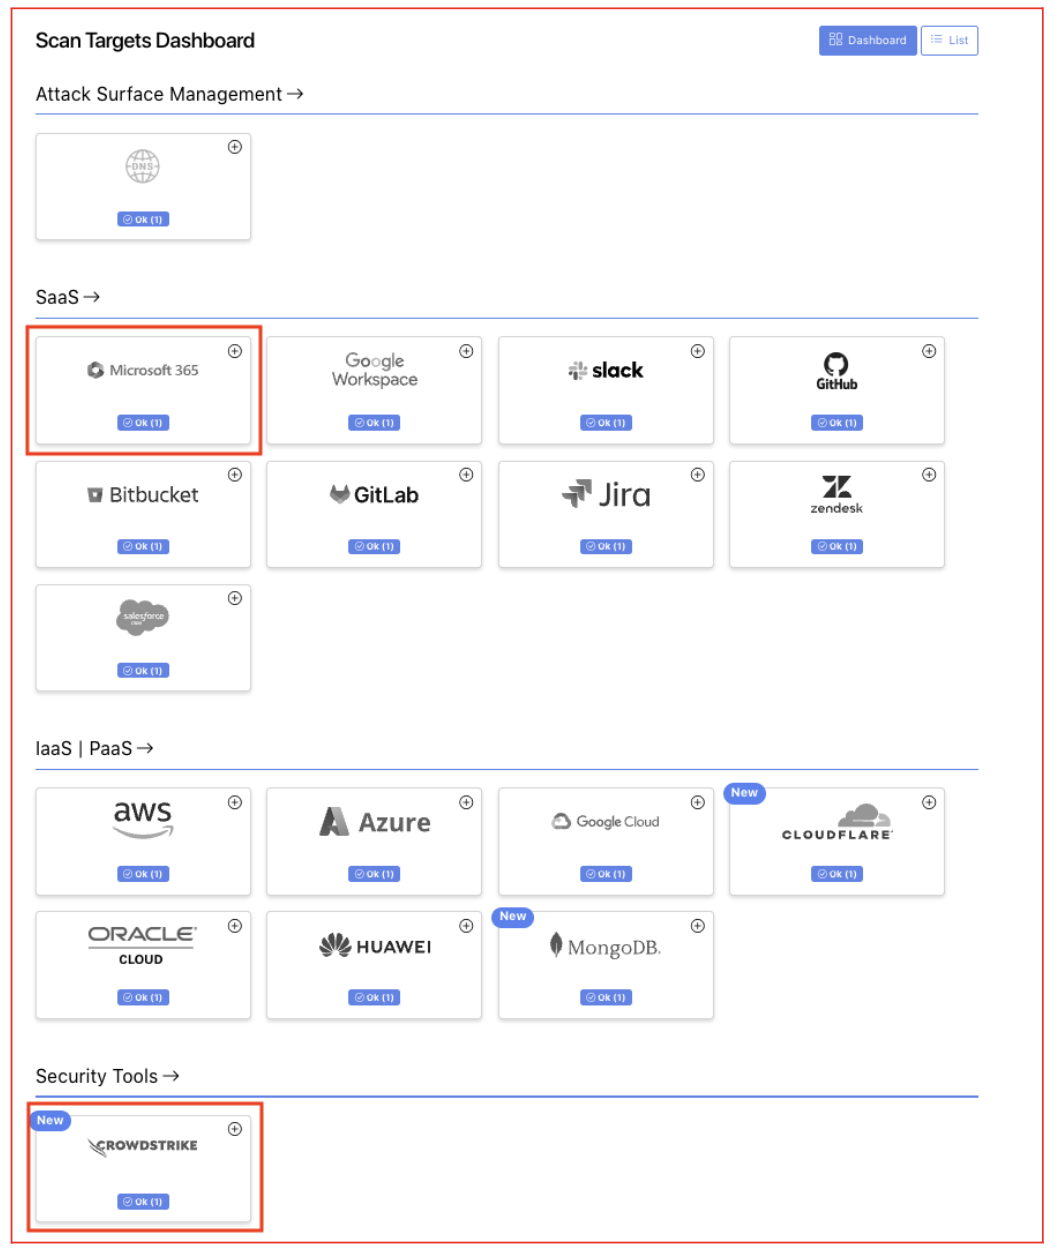
Crowdstrike Falcon: A cybersecurity platform that provides cloud-native endpoint protection, threat intelligence, and incident response services. You can find this Scan Target Type under the new section Security Tools in the Scan Targets Dashboard.
Microsoft Defender for Endpoint: An enterprise-grade endpoint security solution and a key component of the Microsoft Security suite. In Zanshin, the predefined security checks for Microsoft Defender are seamlessly executed as part of Microsoft 365 scans. This integration operates transparently, requiring no additional action from the user.
As usual, Zanshin will scan these platforms without ever having access to your sensitive data. We simply ask for the minimal set of permissions to review security-relevant settings to ensure you stay as safe as possible.
New filters available in Dashboard and Alerts lists
New filtering options were introduced in Zanshin to help you quickly find the most relevant information in your dashboards and alerts lists. These enhancements will provide greater control and efficiency when reviewing security data.
- You can filter information by Scan Target Tags or Scan Target names (up to 10 items), in:
- My Organization Dashboard
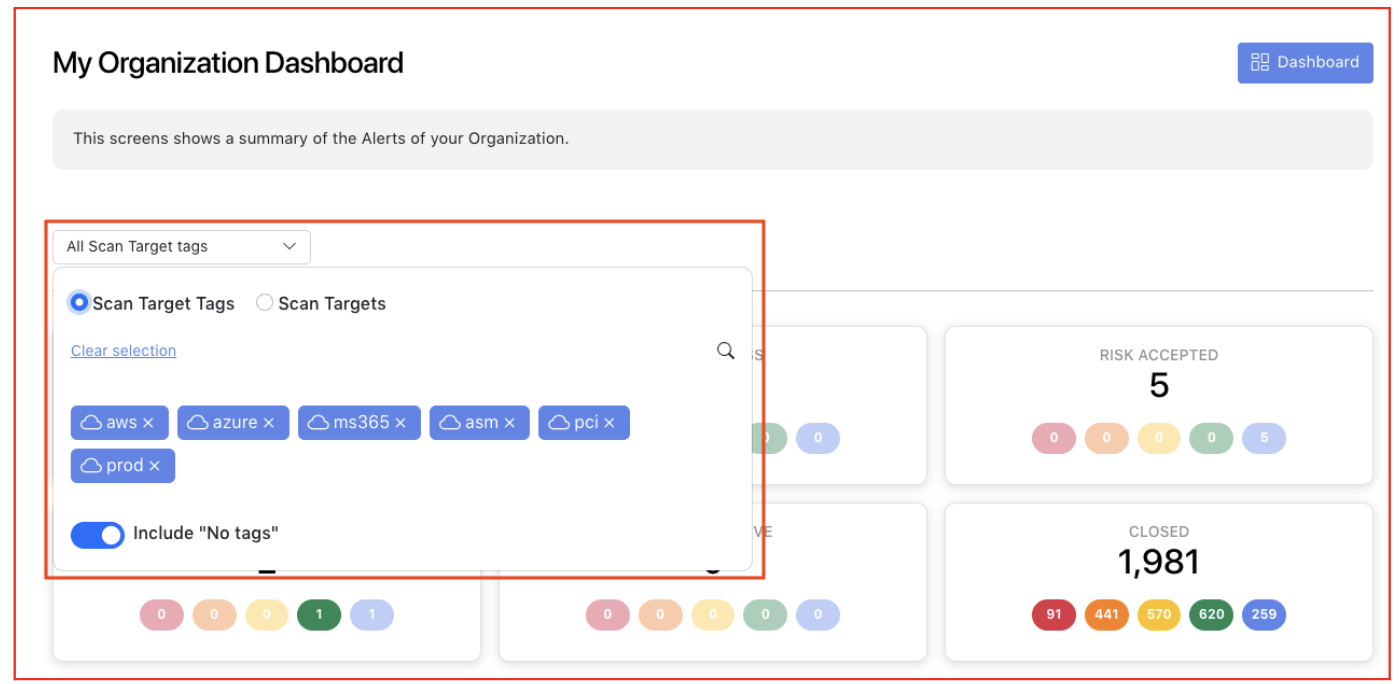
My Organization Alerts
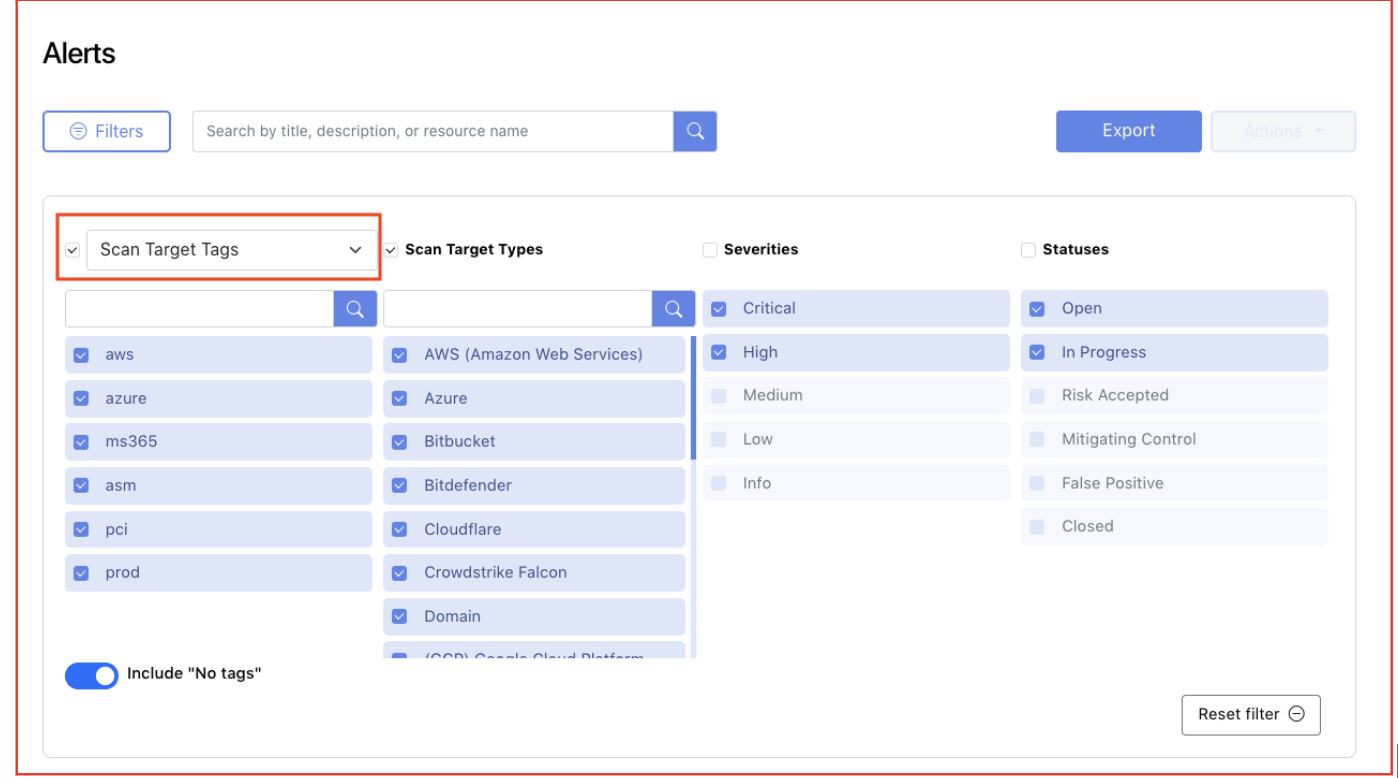
- Similarly, if you are monitoring your Following Organizations, you can now filter this dashboard by Following Organization Tags or Following Organization Names (up to 10 items).
- Following Alerts Dashboard
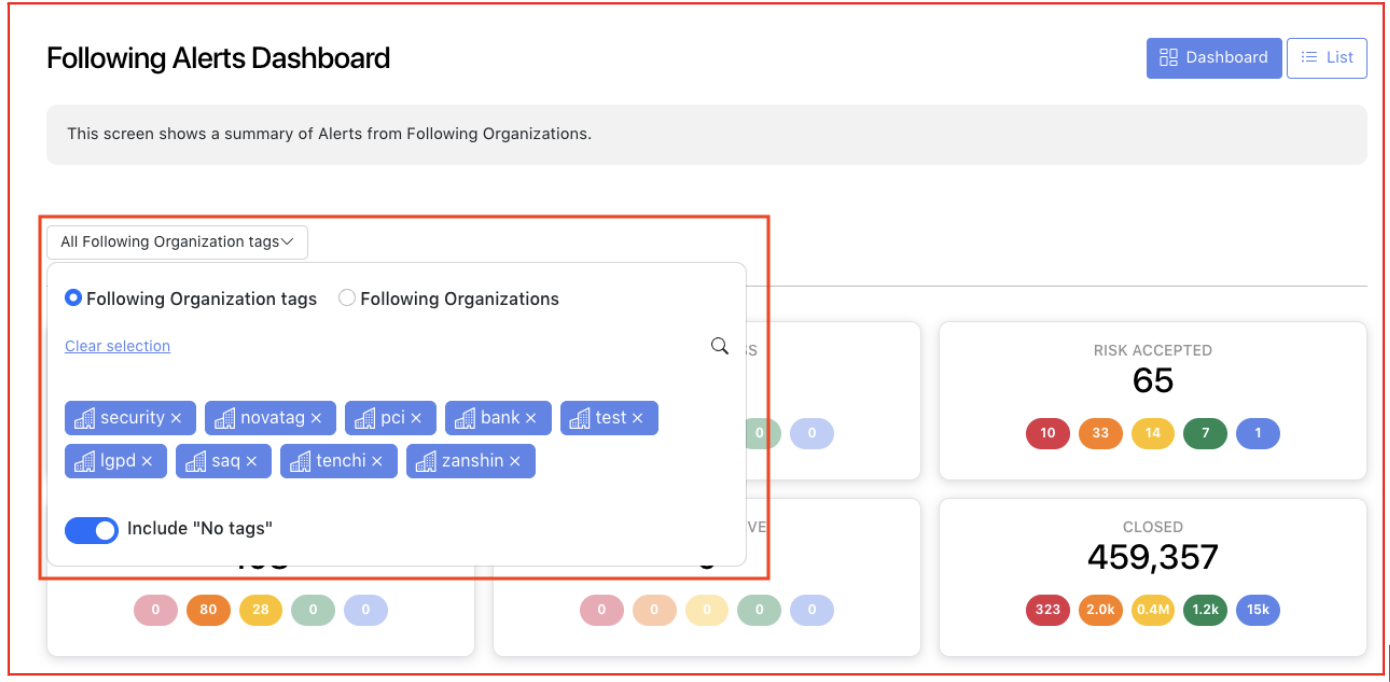
Following Organization Alerts
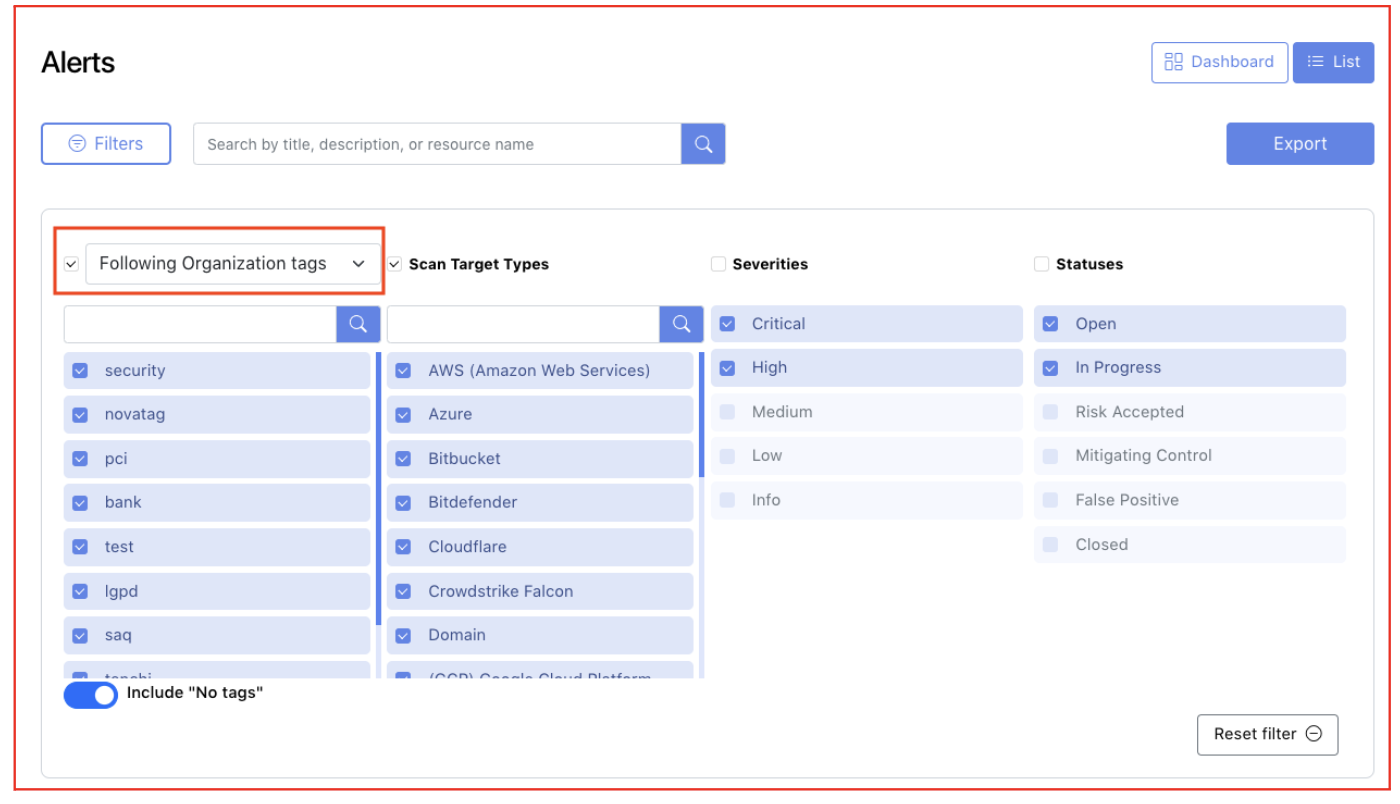
Zanshin Rule detection improvements
We have introduced an enhancement in the "IP Address with bad reputation detected" Rule, in order to help identify potential threats and take proactive measures to protect the network and systems from malicious activities. As a result, new alerts may be triggered based on this enhanced detection capability.
Navigation to Alerts is now restored
We want to inform you that the Navigation to Alerts, which was previously impacted by an issue reported in January, has now been fully restored. You can once again drill-down seamlessly to the ‘Alerts List’ from Compliance KPIs and Dashboards, with preset filters applied for a more efficient experience.
Recent Updates | April/25
I am thrilled to announce some exciting new features that will significantly enhance our product's capabilities:
Organization Score
IBM Cloud and Bitdefender scanning support
Please reach out to the Customer Success team to enable these new features for your organization immediately. In the next few days, you will be able to view your organization's score. However, to enable viewing the score of your third parties (Following Organizations), please contact the Customer Success team.
Organization Score
Check out the teaser: https://www.youtube.com/watch?v=wHcR0zqTHqc
The Score is a comprehensive metric designed to provide an easy-to-understand assessment of an organization’s security posture. It is calculated by weighing a variety of factors based on the automated tests performed by Zanshin on your Scan Targets.
The design of the Score was a joint project between Tenchi Security's own engineering and data science teams supported by the deep expertise of the Cyentia Institute, one of the leading organizations globally in the application of data science to information security.
Our Score combines a variety of factors that take into account the number of active Alerts and their relative Severities; the age of the active Alerts and the timeliness with which the Organization has fixed Alerts historically; the number of Alerts that have been reopened; the relative density of Alerts based on the number of assets Zanshin sees during its scans.
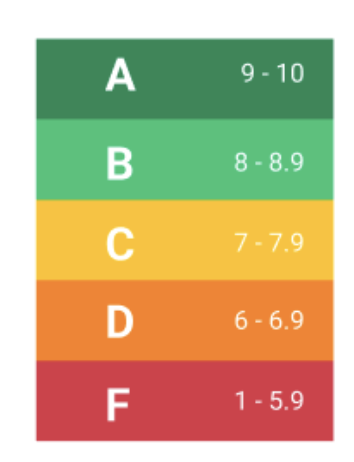
The scoring system uses both a numerical and a letter scale. The numerical scale ranges from 1.0 to 10.0, where 1.0 is the lowest and 10.0 is the highest score. The letter scale consists of A, B, C, D, and F, where A is the highest and F is the lowest Score.
The Score that first-parties (Follower Organizations) see for their third-parties (Following Organizations) is determined by the specific Scan Target visibility of that relationship. If an Organization has ten Scan Targets but only shares three of them with a Follower, the Score that Follower sees is representative only of those three Scan Targets.
The Scores of third-parties are visible to first-party users across multiple pages within Zanshin, including the Following Dashboard, Organizations List and Organization Details pages:
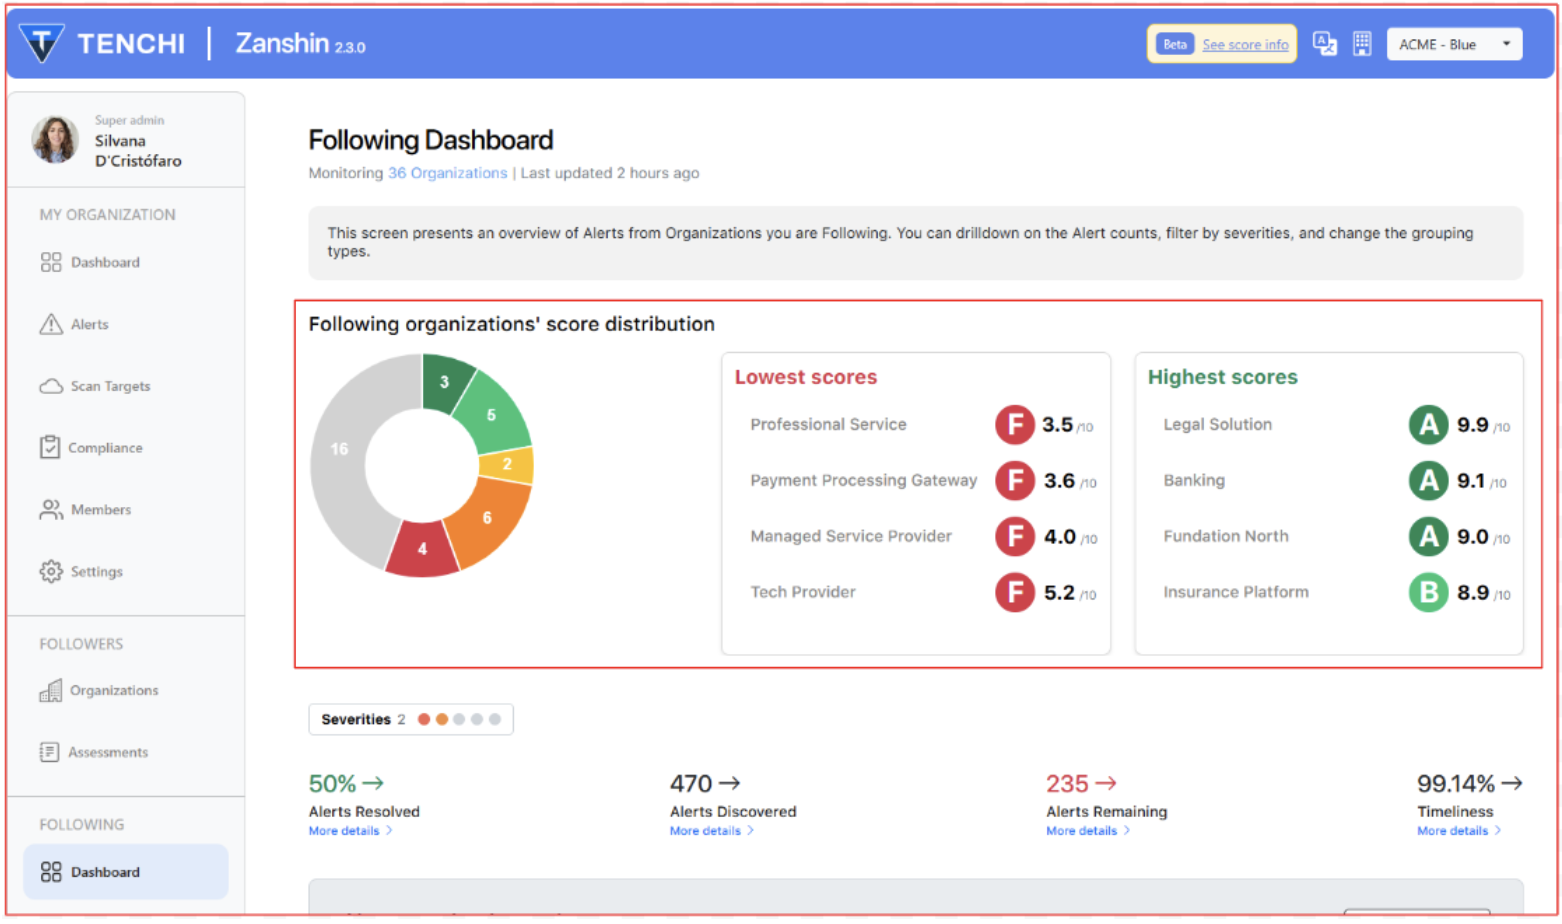
The Following Dashboard below displays the score distribution of third-party organizations. It also identifies the five organizations with the highest and lowest Scores.
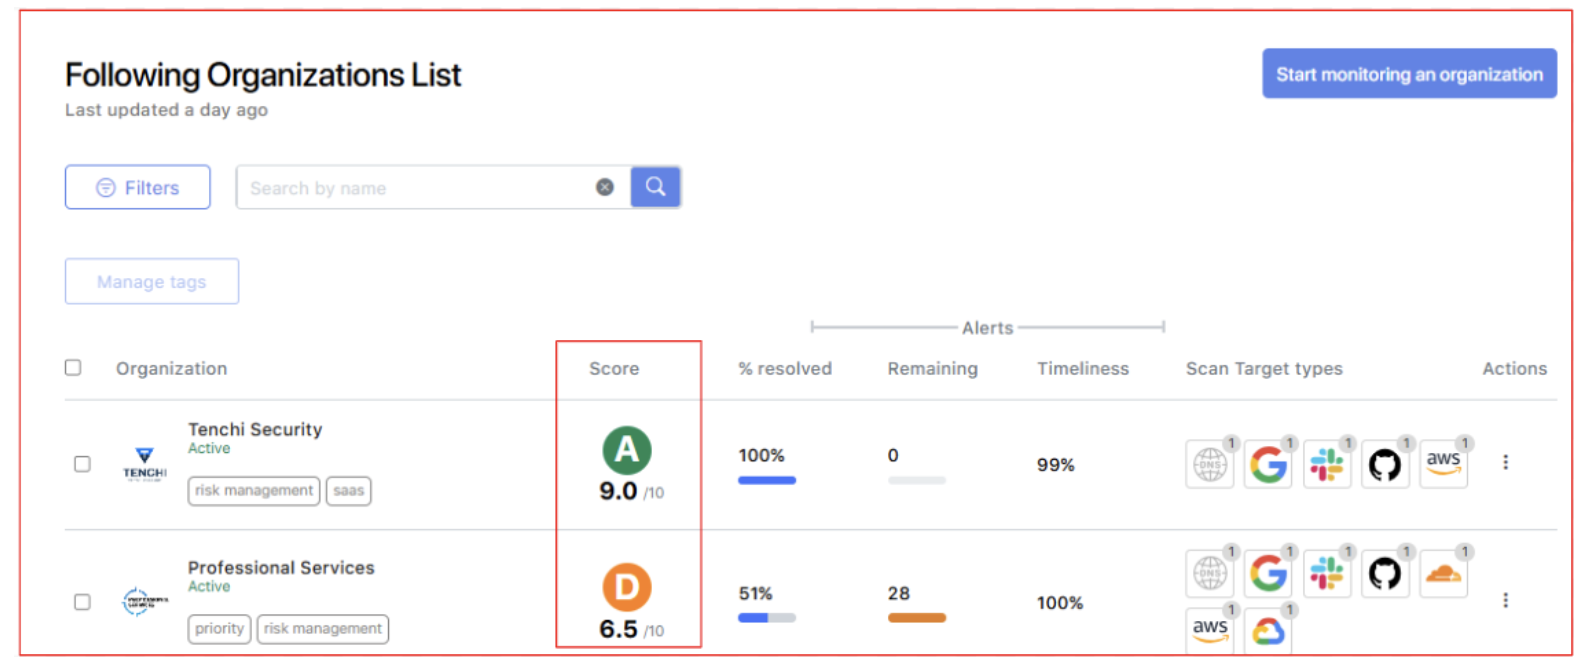
The list of Following Organizations below is displayed with their scores. The "Score" column can be sorted in ascending or descending order.
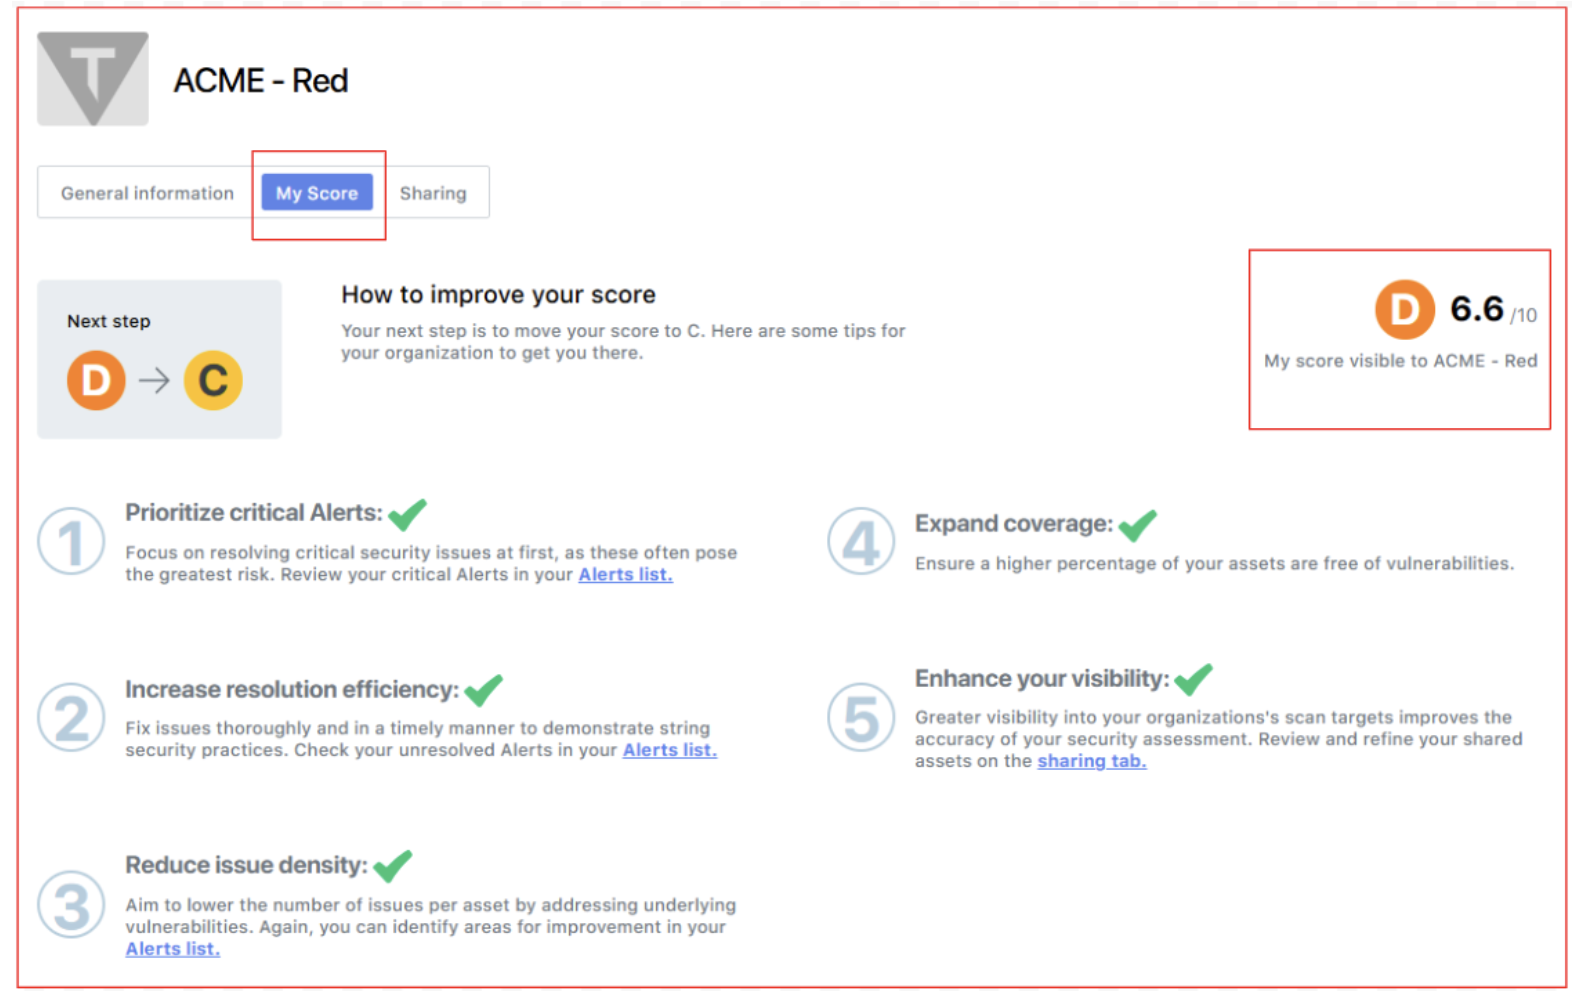
The Following Organization Details page also displays the Score, which is based on the Scan Targets that this Following organization shares with its Follower.

On the My Organization Dashboard, Zanshin organizations can now view their own Score, based on all their Scan Targets, and the Score distribution as seen by their Follower Organizations. Remember that the score may vary for Follower Organizations depending on which Scan Targets are shared with them:

The Followers page and Follower Organization Details page will display my Score as viewed by my Follower Organizations.

Domain Scan Targets creation
Tenchi will ensure that every organization has a Score by creating one or more Domain Scan Targets for any organization currently lacking one. Findings related to Domain Scan Targets are now visible to all licensed Zanshin Organizations, as they are based on public data, and they will also be used in the Score calculation.
IBM Cloud and Bitdefender scanning support
We’re excited to share that Zanshin now supports two new Scan Target types: IBM Cloud and Bitdefender! This update expands our platform’s capabilities, giving you even greater visibility into your third-party ecosystem and enabling more comprehensive risk assessments.
What’s New?
IBM Cloud: it is a leading enterprise cloud platform offering IaaS and PaaS solutions for building, running, and managing applications and services. With our new scanning support, Zanshin can now assess security configurations, helping you reduce risk across a broader range of infrastructure.
Bitdefender: it provides industry-leading cybersecurity solutions, including endpoint protection, detection and response, and threat prevention. By supporting Bitdefender as a scan target, Zanshin enables visibility into the security posture and alert status of third parties using this platform, enhancing your ability to monitor defenses against malware and advanced threats.

As usual, Zanshin will scan these platforms without ever having access to your sensitive data, simply asking for the minimal set of permissions to review security-relevant settings to ensure you stay as safe as possible.
Recent product updates | March/25
We are reaching out to share exciting updates related to Domain Scan Targets in Zanshin, designed to enhance transparency, control, and overall user experience.
Why is this changing?
We are continuously working to improve your experience in Zanshin. These updates are designed to enhance visibility, accuracy, and user control over Domain Scan Targets, aligning our platform with industry best practices.
What is changing?
New modes for Domain Scan Targets
Changes to remove a Domain Scan Target
New modes for Domain Scan Targets
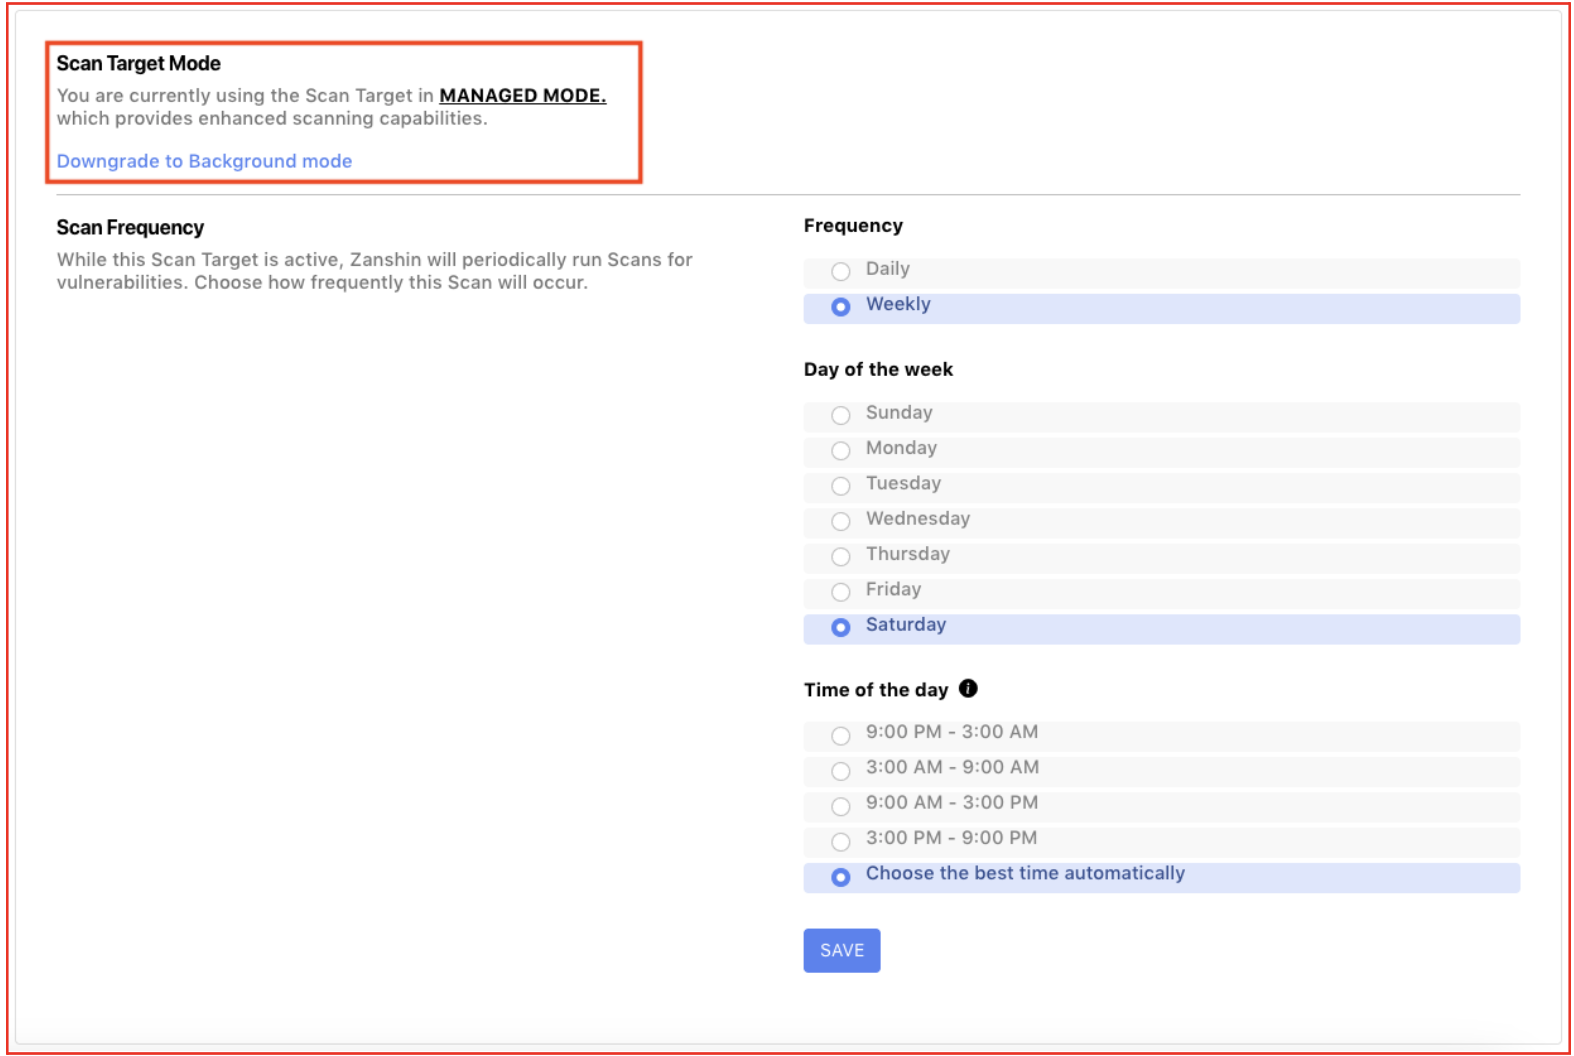
We have introduced two different modes for Domain Scan Targets. This information is shown on the Domain Scan Targets Details Page, under the Settings tab:
- Managed Mode (Recommended)
- Provides deeper insights and uncovers more complex issues.Offers higher accuracy in Scan Target results.Allows control over scan frequency.Ability to initiate scans at any time.
- Background Mode
- Provides a broad overview focusing on less resource-intensive checks.Scan Frequency options are disabled in this mode.
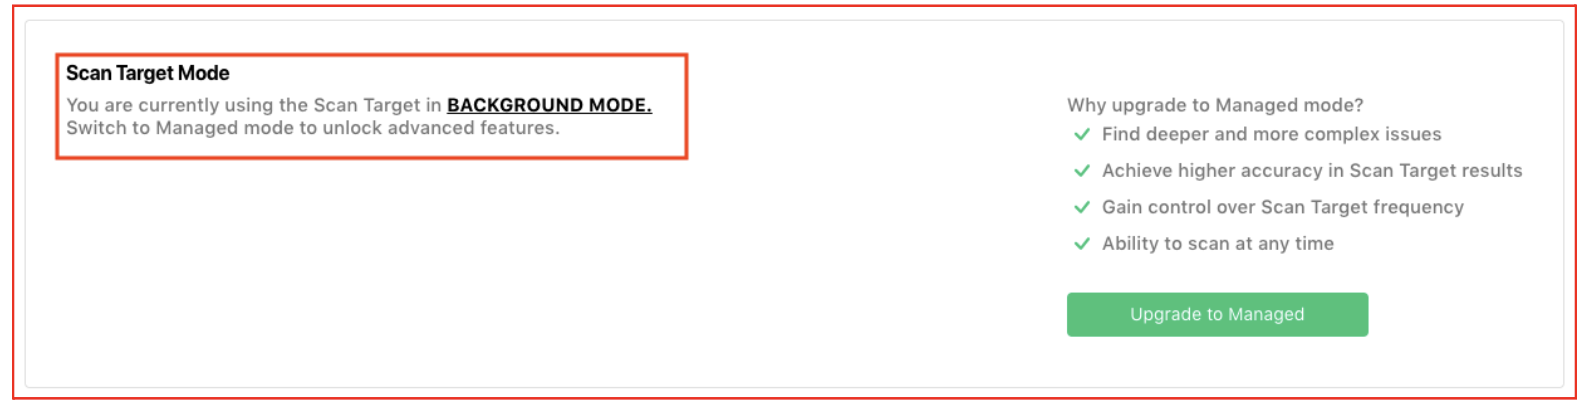
Currently, all existing Domain Scan Targets are set to Managed mode. While you can switch from Managed mode to Background mode at any time, we strongly recommend keeping them in Managed mode for the most comprehensive and accurate monitoring.
Newly created Domain Scan Targets are initially set to Background mode. To enable Managed mode, we must validate the domain to confirm that your organization has control over it. This validation process is essential to verify domain ownership and ensure accurate monitoring.
Changes to remove Domain Scan Targets
As previously communicated, visibility for Domain Scan Targets has changed.
Since the findings related to Domain Scan Targets are based on public data, they will now be visible to all licensed Organizations in Zanshin. This will provide a more streamlined way to showcase your domain’s security performance and compliance, and bring Zanshin in line with widespread industry practice. This allows your Organization to build trust and demonstrate security best practices to your customers and partners.
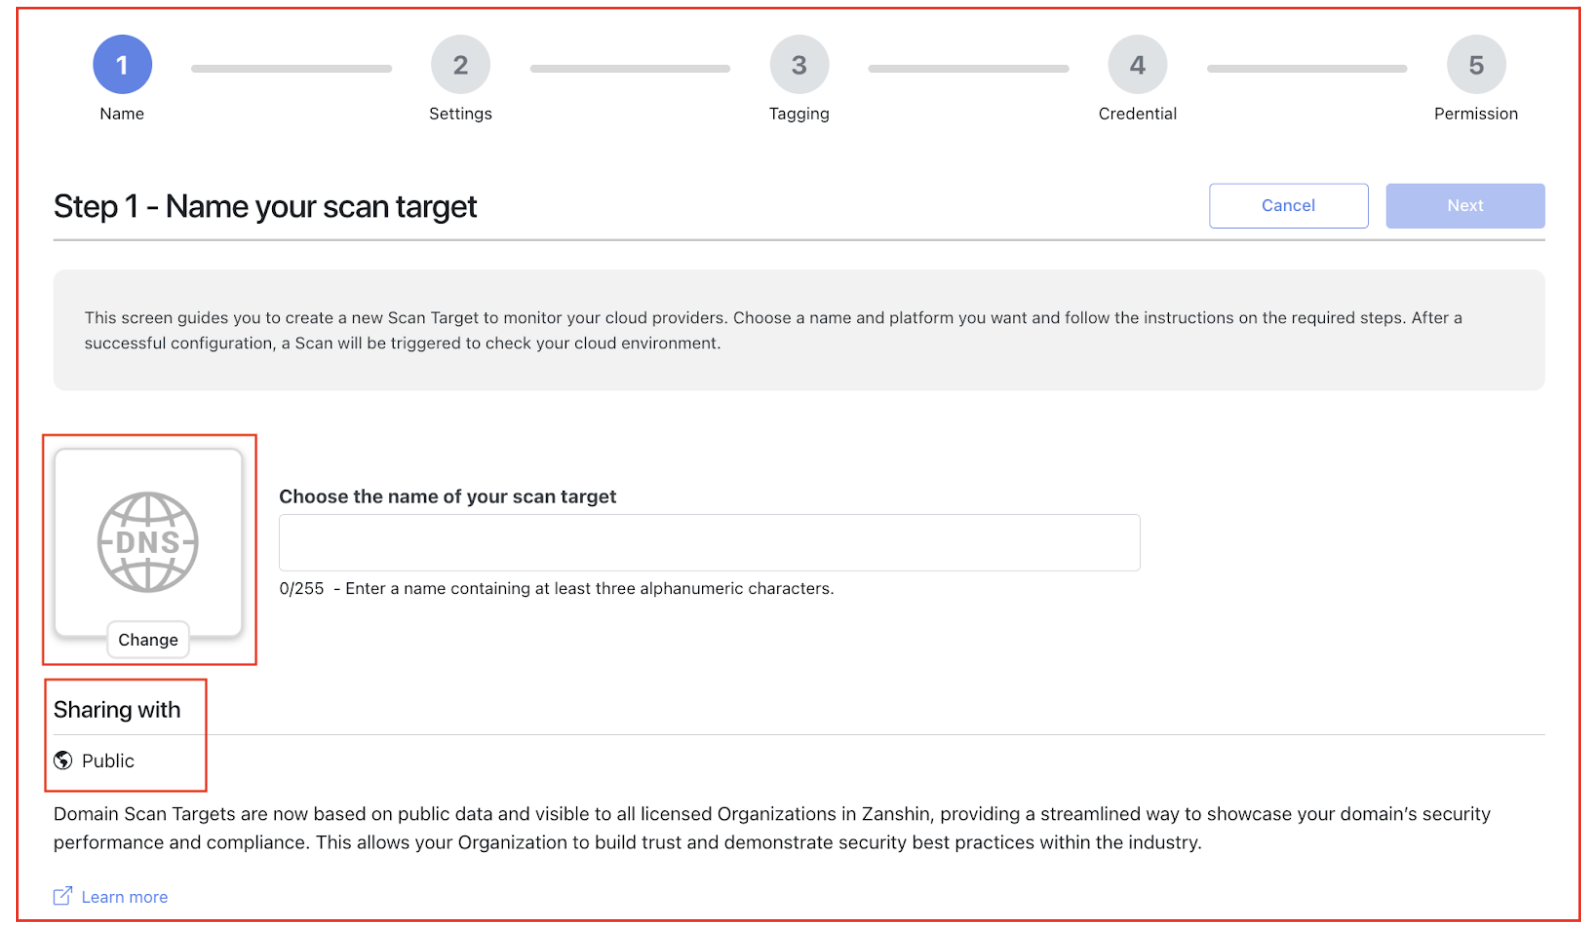
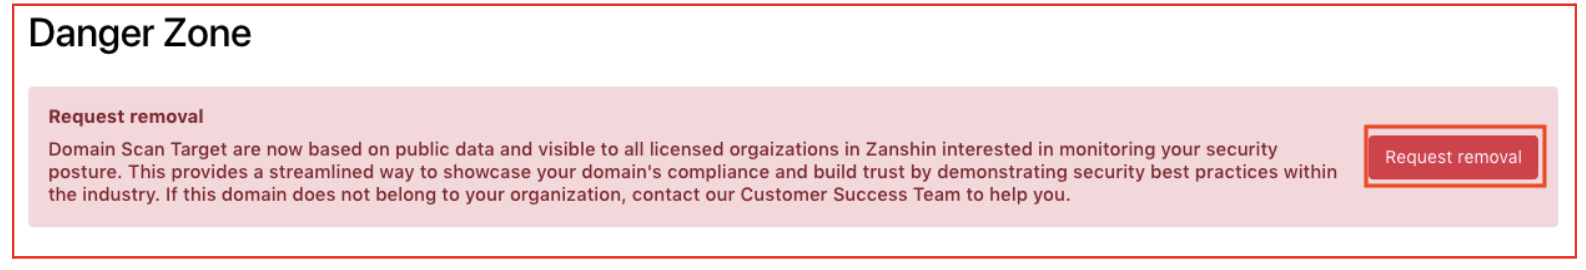
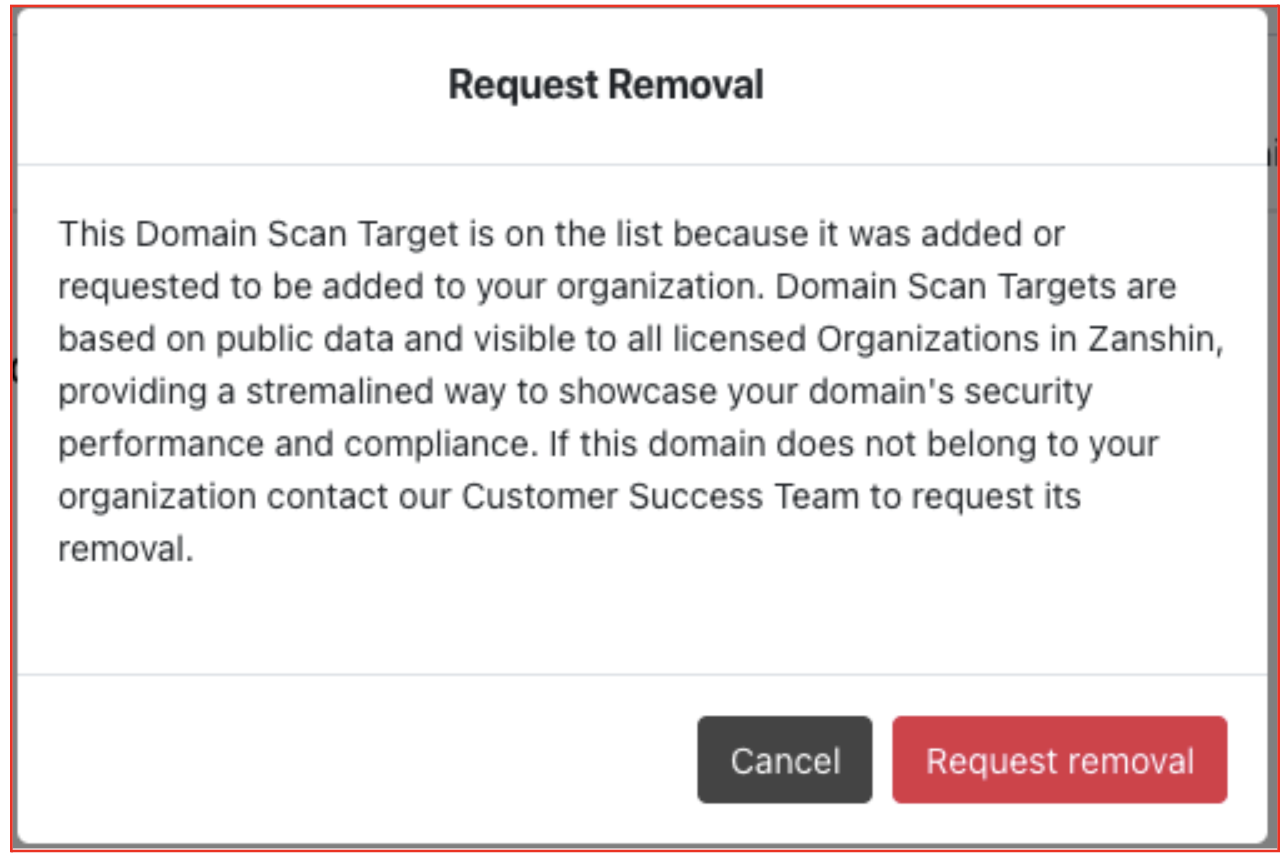
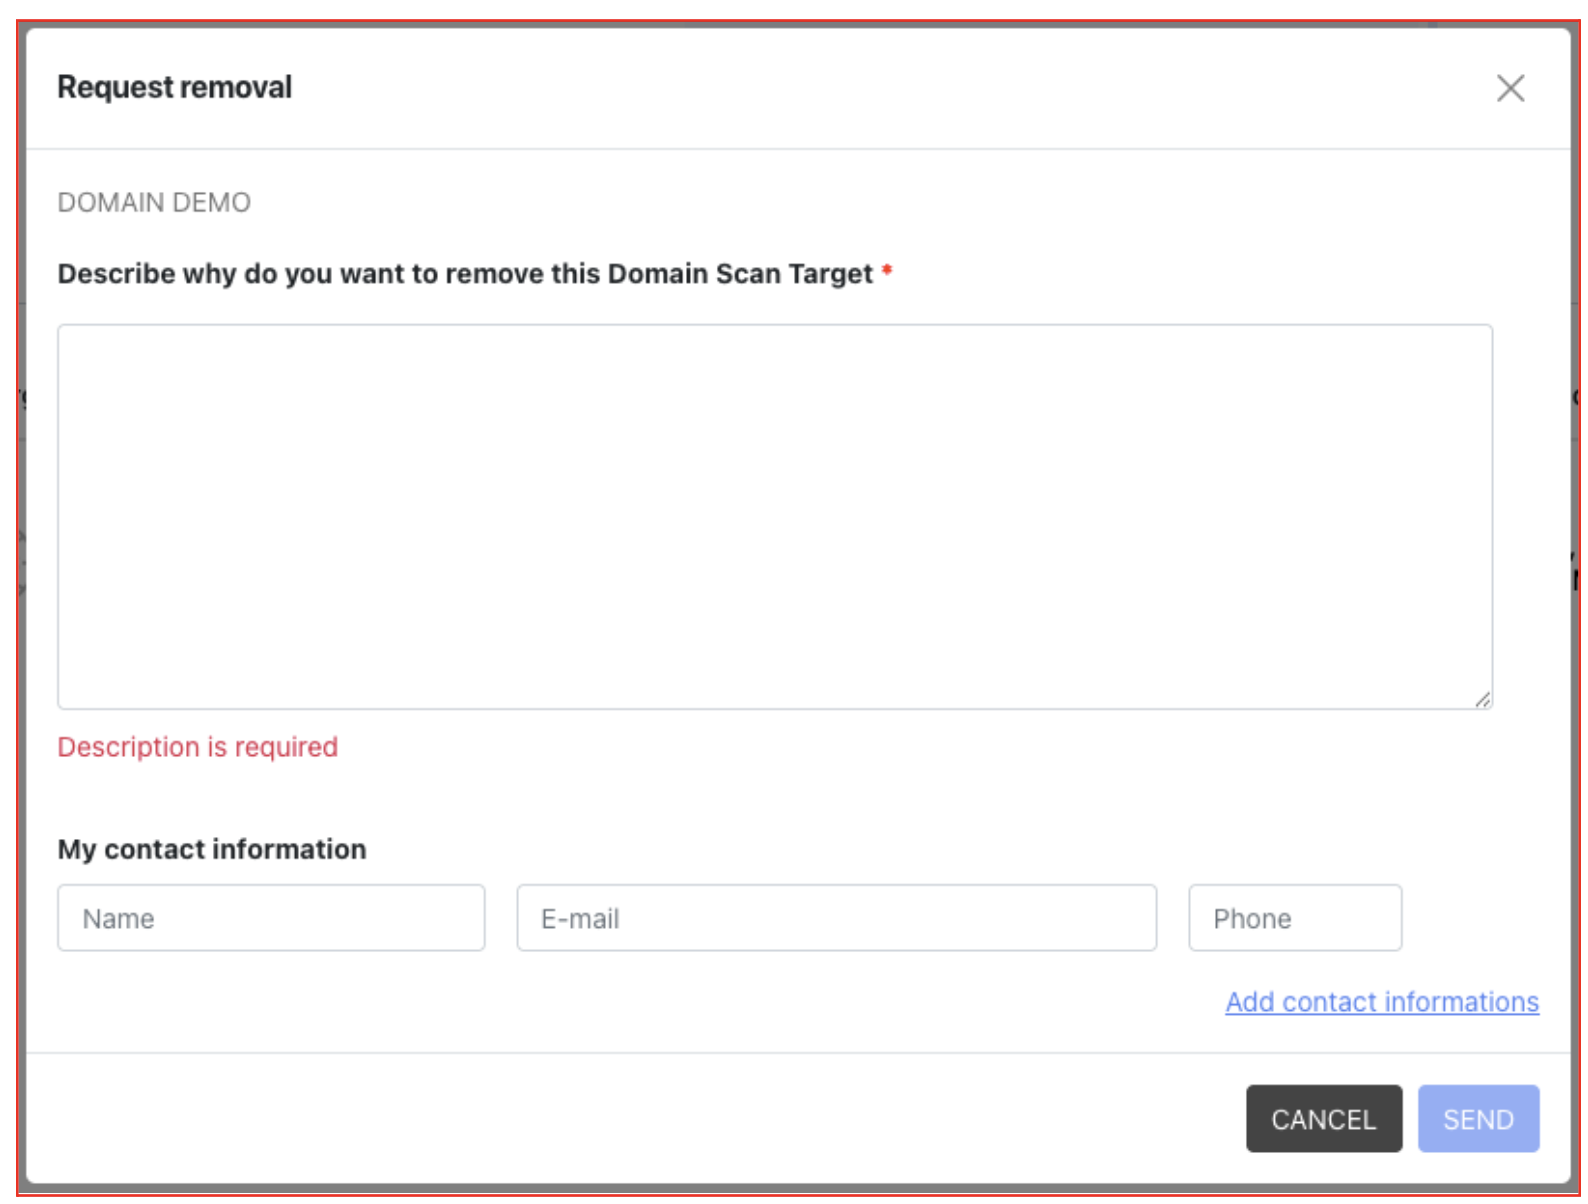
In alignment with the visibility of Domain Scan Targets, now users can no longer directly remove them. Instead, users can request to remove them. This request will be handled by our Customer Success Team, who will evaluate the case and communicate the outcome.
To facilitate this process, a new option “Why is this here?” is now available in the Scan Target list, for Domain Scan Targets.
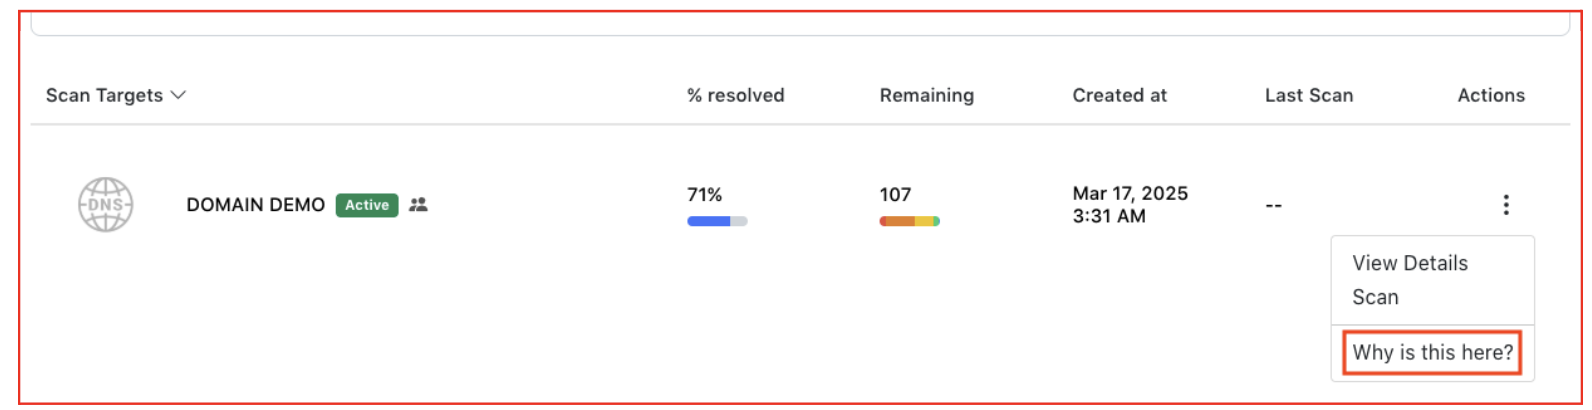
Selecting this option will provide an explanation about why the Domain Scan Target is listed and offer a way to contact our Customer Success Team if you wish to proceed with a removal request:
Users can then proceed to submit a request to remove the Domain Scan Target:
This option is also available on the Domain Scan Targets Details Page, under the Settings tab: